Posts

Showing posts with the label Malware

Blobrunner - Apace Debug Shellcode Extracted During Malware Analysis
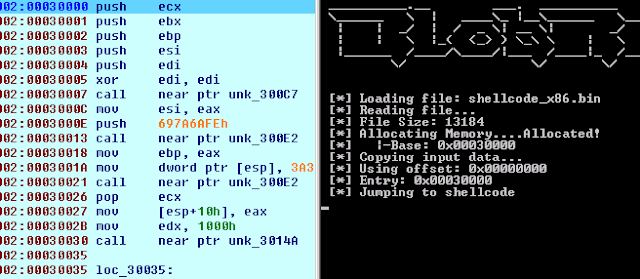
Image
BlobRunner is a uncomplicated tool to speedily debug shellcode extracted during malware analysis. BlobRunner allocates retentivity for the target file in addition to jumps to the base of operations (or offset) of the allocated memory. This allows an analyst to speedily debug into extracted artifacts amongst minimal overhead in addition to effort. To role BlobRunner, you lot tin download the compiled executable from the releases page or fix your ain using the steps below. Building Building the executable is conduct forrad in addition to relatively painless. Requirements Download in addition to install Microsoft Visual C++ Build Tools or Visual Studio Build Steps Open Visual Studio Command Prompt Navigate to the directory where BlobRunner is checked out Build the executable past times running: cl blobrunner.c Building BlobRunner x64 Building the x64 version is most the same equally above, but only uses the x64 tooling. Open x64 Visual Studio Command Prompt...

Domain Hunter - Checks Expired Domains For Categorization/Reputation As Well As Archive.Org History To Own Upward One's Heed Skilful Candidates For Phishing As Well As C2 Domain Names

Image
Domain refer choice is an of import seem of training for penetration tests as well as specially Red Team engagements. Commonly, domains that were used previously for benign purposes as well as were properly categorized tin endure purchased for alone a few dollars. Such domains tin allow a squad to bypass reputation based spider web filters as well as network egress restrictions for phishing as well as C2 related tasks. This Python based tool was written to speedily inquiry the Expireddomains.net search engine for expired/available domains amongst a previous history of use. It as well as then optionally queries for domain reputation against services similar Symantec WebPulse (BlueCoat), IBM X-Force, as well as Cisco Talos. The primary tool output is a timestamped HTML tabular array means report. Changes 5 Oct 2018 Fixed logic for filtering domains amongst desirable categorizations. Previously, or hence fault weather weren't filtered as well as would lawsuit inwards do...

Malcom - Malware Communications Analyzer

Image
Malcom is a tool designed to analyze a system's network communication using graphical representations of network traffic, as well as cross-reference them amongst known malware sources. This comes handy when analyzing how sure enough malware species endeavour to communicate amongst the exterior world. What is Malcom? Malcom tin flame assistance you: detect primal command as well as command (C&C) servers understand peer-to-peer networks observe DNS fast-flux infrastructures quickly create upwardly one's heed if a network artifact is 'known-bad' The aim of Malcom is to brand malware analysis as well as intel gathering faster past times providing a human-readable version of network traffic originating from a given host or network. Convert network traffic information to actionable intelligence faster. Check the wiki for a Quickstart amongst closed to dainty screenshots as well as a tutorial on how to add together your ain feeds . If yous demand closed...

Imaginaryc2 - Tool Which Aims To Aid Inwards The Behavioral (Network) Analysis Of Malware

Image
author: Felix Weyne ( website ) ( Twitter ) Imaginary C2 is a python tool which aims to assistance inward the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures HTTP requests towards selectively chosen domains/IPs. Additionally, the tool aims to larn inward slow to replay captured Command-and-Control responses/served payloads. By using this tool, an analyst tin feed the malware consistent network responses (e.g. C&C instructions for the malware to execute). Additionally, the analyst tin capture as well as inspect HTTP requests towards a domain/IP which is off-line at the fourth dimension of the analysis. Replay package captures Imaginary C2 provides 2 scripts to convert packet captures (PCAPs) or Fiddler Session Archives into request definitions which tin survive parsed yesteryear imaginary C2. Via these scripts the user tin extract HTTP asking URLs as well as domains, every bit good every bit HTTP responses. This way...

Ustealer - Ubuntu Stealer, Pocket Ubuntu Data Inwards Local Pc

Image
Ubuntu stealer, pocket ubuntu information inwards local pc (nice alongside usb key) Require G++ sudo apt-get install g++ libsqlite3 sudo apt-get install libsqlite3-dev Compilation Go inwards Ustealer/ folder as well as function makefile make Use ./ustealer Download Ustealer

Pe-Sieve - Recognizes In Addition To Dumps A Diversity Of Potentially Malicious Implants (Replaced/Injected Pes, Shellcodes, Hooks, In-Memory Patches)

Image
PE-sieve is a light-weight tool that helps to detect malware running on the system, equally good equally to collect the potentially malicious fabric for farther analysis. Recognizes in addition to dumps diversity of implants inside the scanned process: replaced/injected PEs, shellcodes, hooks, in addition to other in-memory patches. Detects inline hooks, Process Hollowing, Process Doppelgänging, Reflective DLL Injection, etc. uses library: https://github.com/hasherezade/libpeconv.git Clone: Use recursive clone to larn the repo together alongside the submodule: git clone --recursive https://github.com/hasherezade/pe-sieve.git Latest builds*: *those builds are available for testing in addition to they may last ahead of the official release : 32-bit 64-bit Download Pe-Sieve

Malice - Virustotal Wanna Move (Now Alongside 100% To A Greater Extent Than Hipster)

Image
Malice's mission is to live a costless opened upwards source version of VirusTotal that anyone tin give notice role at whatever scale from an independent researcher to a fortune 500 company. Try It Out DEMO: demo.malice.io username : malice password : ecilam Requirements Hardware 16GB disk space 4GB RAM Software Docker Getting Started (OSX) Install $ brew install maliceio/tap/malice Usage: malice [OPTIONS] COMMAND [arg...] Open Source Malware Analysis Framework Version: 0.3.11 Author: blacktop - <https://github.com/blacktop> Options: --debug, -D Enable debug trend [$MALICE_DEBUG] --help, -h demo assistance --version, -v impress the version Commands: scan Scan a file lookout Watch a folder lookup Look upwards a file hash elk Start an ELK docker container plugin List, Install or Remove Plugins assistance Shows a listing of commands or assistance for i ascendancy Run ...

Pftriage - Python Tool Together With Library To Aid Analyze Files During Malware Triage Together With Analysis

Image
pftriage is a tool to assist analyze files during malware triage. It allows an analyst to apace thought in addition to extract properties of a file to assist during the triage process. The tool also has an analyze purpose which tin give the axe divulge mutual malicious indicators used yesteryear malware. Dependencies pefile filemagic Note: On Mac - Apple has implemented their ain version of the file command. However, libmagic tin give the axe last installed using homebrew $ brew install libmagic Usage usage: pftriage [options] Show information nearly a file for triage. positional arguments: file The file to triage. optional arguments: -h, --help demo this assist message in addition to popular off -i, --imports Display import tree -s, --sections Display overview of sections. For to a greater extent than detailed information top the -v switch --removeoverlay Remove overlay data. --extr...

Ponce - Ida Plugin For Symbolic Execution Only One-Click Away!

Image
Ponce (pronounced [ 'poN θe ] pon-they ) is an IDA Pro plugin that provides users the mightiness to perform taint analysis too symbolic execution over binaries inward an slow too intuitive fashion. With Ponce y'all are 1 click away from getting all the mightiness from cutting border symbolic execution. Entirely written inward C/C++. Why? Symbolic execution is non a novel concept inward the safety community. It has been some for years but it is non until the terminal duad of years that opened upwards source projects similar Triton too Angr stimulate got been created to address this need. Despite the availability of these projects, halt users are oftentimes left to implement specific usage cases themselves. We addressed these needs past times creating Ponce, an IDA plugin that implements symbolic execution too taint analysis inside the most used disassembler/debugger for contrary engineers. Installation Ponce plant amongst both x86 too x64 binaries inward ...

Osint-Spy - Search Using Osint (Open Rootage Intelligence)

Image
Performs OSINT scan on email/domain/ip_address/organization using OSINT-SPY. It tin hold upward used past times Data Miners, Infosec Researchers, Penetration Testers too cyber criminal offence investigator inwards social club to uncovering deep information close their target. OSINT-SPY Documentation (beta) File Name : README Author : @sk_security Version : 0.0.1 Website : osint-spy.com Overview of this tool: Perform scan on IP Address / domain / e-mail address / BTC(bitcoin) address / device Find out latest bitcoin block information List out all the ciphers supported past times especial website too server Check whether a especial website is vulnerable to heartbleed or non ? Dump all the contacts too messages from skype database Analyze malware or malicous file remotely Licenses information OSINT-SPY too its documents are covered alongside GPL-3.0 (General Public License v3.0) Using OSINT-SPY @@@@@@@@@ @@@@@@@@@ | ...

Iot-Home-Guard - A Tool For Malicious Quest Detection Inwards Iot Devices

Image
IoT-Home-Guard is a projection to attention people discovery malware inwards smart habitation devices. For users the projection tin forcefulness out attention to abide by compromised smart habitation devices. For safety researchers it is also useful inwards network analysis together with malicious hehaviors detection. In July 2018 nosotros had completed the get-go version. We volition consummate the minute version yesteryear Oct 2018 amongst improvement of user sense together with increased expose of identifiable devices. The get-go generation is a hardware device based on Raspberry Pi amongst wireless network interface controllers. We volition customize novel hardware inwards the minute generation. The organization tin forcefulness out hold out educate amongst software purpose inwards laptops subsequently essential environs configuration. Software purpose is available inwards software_tools/. Proof of principle Our approach is based on the detection of malicious network tra...