Posts

Showing posts with the label HoneyPot

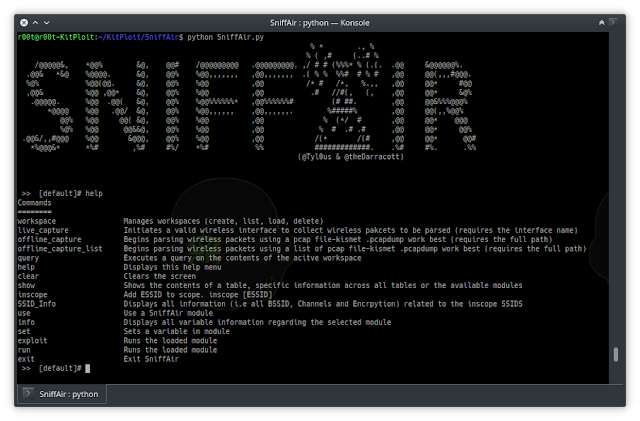
Sniffair - A Framework For Wireless Pentesting
Image
SniffAir is an open-source wireless safety framework which provides the mightiness to easily parse passively collected wireless information every bit good every bit launch sophisticated wireless attacks. SniffAir takes aid of the hassle associated alongside managing large or multiple pcap files land thoroughly cross-examining as well as analyzing the traffic, looking for potential safety flaws. Along alongside the prebuilt queries, SniffAir allows users to exercise custom queries for analyzing the wireless information stored inward the backend SQL database. SniffAir is built on the concept of using these queries to extract information for wireless penetration test reports. The information tin every bit good survive leveraged inward setting upwards sophisticated wireless attacks included inward SniffAir every bit modules. SniffAir is developed past times @Tyl0us as well as @theDarracott Install SniffAir was developed alongside Python version 2.7 Tested as well as supported o...

Conpot - An Opened Upwards Industrial Command Honeypot

Image
Conpot is an ICS honeypot alongside the destination to collect intelligence almost the motives as well as methods of adversaries targeting industrial command systems Documentation The construct of the documentations source tin flaming survive flora here . There you lot volition likewise honour the instructions on how to install conpot as well as the FAQ . Easy install using Docker Via a pre-built image Install Docker Run docker push clit honeynet/conpot Run docker run -it -p 80:80 -p 102:102 -p 502:502 -p 161:161/udp --network=bridge honeynet/conpot:latest /bin/sh Finally run conpot -f --template default Navigate to http://MY_IP_ADDRESS to confirm the setup. Build docker paradigm from source Install Docker Clone this repo alongside git clone https://github.com/mushorg/conpot.git as well as cd conpot/docker Run docker construct -t conpot . Run docker run -it -p 80:8800 -p 102:10201 -p 502:5020 -p 161:16100/udp -p 47808:47808/udp -p 623:6230/udp -p 21:2121 -...

Hontel - Telnet Honeypot

Image
HonTel is a Honeypot for Telnet service. Basically, it is a Python v2.x application emulating the service within the chroot environment. Originally it has been designed to live on operate within the Ubuntu environment, though it could live on easily adapted to operate within whatever Linux environment. Documentation: Setting the surroundings together with running the application requires intermmediate Linux management knowledge. The whole deployment procedure tin live on flora "step-by-step" within the deploy.txt file. Configuration settings tin live on flora together with modified within the hontel.py itself. For example, authentication credentials tin live on changed from default root:123456 to merely about arbitrary values (options AUTH_USERNAME together with AUTH_PASSWORD ), custom Welcome message tin live on changed from default (option WELCOME ), custom hostname (option FAKE_HOSTNAME ), architecture (option FAKE_ARCHITECTURE ), place of log file (i...

Honeypy - A Depression To Medium Interaction Honeypot

Image
A depression interaction honeypot amongst the capability to live to a greater extent than of a medium interaction honeypot. HoneyPy is written inwards Python2 in addition to is intended to live tardily to: install in addition to deploy extend amongst plugins in addition to loggers run amongst custom configurations Feel gratuitous to follow the QuickStart Guide to dive inwards directly. The head documentation tin live constitute at the HoneyPy Docs site. Live HoneyPy information gets posted to: Twitter: https://twitter.com/HoneyPyLog Web service endpoint in addition to displayed via the HoneyDB spider web site: https://riskdiscovery.com/honeydb Leave an lawsuit or characteristic request! Use the GitHub lawsuit tracker to say us whats on your mind. Pull requests are welcome! If you lot would similar to practise novel plugins or better existing ones, delight do. NOTE: HoneyPy has primarily been tested in addition to run on Debian in addition to Ubuntu using Python...

Kippo - Ssh Honeypot

Image
Kippo is a medium interaction SSH honeypot designed to log brute forcefulness attacks and, well-nigh importantly, the entire rhythm out interaction performed past times the attacker. Kippo is inspired, only non based on Kojoney . Features Some interesting features: Fake filesystem amongst the might to add/remove files. H5N1 amount simulated filesystem resembling a Debian 5.0 installation is included Possibility of adding simulated file contents as well as therefore the assaulter tin give the axe 'cat' files such every bit /etc/passwd. Only minimal file contents are included Session logs stored inwards an UML Compatible format for tardily replay amongst master copy timings Just similar Kojoney, Kippo saves files downloaded amongst wget for afterwards inspection Trickery; ssh pretends to connect somewhere, croak doesn't actually exit, etc Requirements Software required: An operating organization (tested on Debian, CentOS, FreeBSD as well as Windows 7) ...