Posts

Showing posts with the label Security

Robber - Tool For Finding Executables Prone To Dll Hijacking

Image
Robber is a costless opened upwardly source tool developed using Delphi XE2 without whatever third political party dependencies. What is DLL hijacking ?! Windows has a search path for DLLs inwards its underlying architecture. If yous tin figure out what DLLs an executable requests without an absolute path (triggering this search process), yous tin as well as then house your hostile DLL somewhere above the search path thence it'll live on constitute earlier the existent version is, as well as Windows volition happilly feed your laid upwardly on code to the application. So, let's pretend Windows's DLL search path looks something similar this: A) . <-- electrical flow working directory of the executable, highest priority, showtime check B) \Windows C) \Windows\system32 D) \Windows\syswow64 <-- lowest priority, final check as well as unopen to executable "Foo.exe" requests "bar.dll", which happens to alive ...

Scannerl - The Modular Distributed Fingerprinting Engine

Image
Scannerl is a modular distributed fingerprinting engine implemented past times Kudelski Security . Scannerl tin give the axe fingerprint thousands of targets on a unmarried host, but tin give the axe precisely every bit easily last distributed across multiple hosts. Scannerl is to fingerprinting what zmap is to port scanning. Scannerl industrial plant on Debian/Ubuntu/Arch (but volition likely locomote on other distributions every bit well). It uses a master/slave architecture where the master copy node volition distribute the locomote (host(s) to fingerprint) to its slaves (local or remote). The entire deployment is transparent to the user. Why job Scannerl When using conventional fingerprinting tools for large-scale analysis, safety researchers volition oftentimes hitting 2 limitations: first, these tools are typically built for scanning comparatively few hosts at a fourth dimension as well as are inappropriate for large ranges of IP addresses. Second, if large hit of IP...

Invisi-Shell - Shroud Your Powershell Script Inwards Manifestly Sight (Bypass All Powershell Safety Features)

Image
Hide your powershell script inwards obviously sight! Invisi-Shell bypasses all of Powershell safety features (ScriptBlock logging, Module logging, Transcription, AMSI) yesteryear hooking .Net assemblies. The claw is performed via CLR Profiler API. Work In Progress This is nevertheless a preliminary version intended equally a POC. The code industrial plant exclusively on x64 processes together with tested against Powershell V5.1. Usage Copy the compiled InvisiShellProfiler.dll from /x64/Release/ folder alongside the ii batch files from the root directory (RunWithPathAsAdmin.bat & RunWithRegistryNonAdmin.bat) to the same folder. Run either of the batch files (depends if yous bring local admin privelledges or not) Powershell console volition run. Exit the powershell using the leave of absence ascendance (DON'T CLOSE THE WINDOW) to permit the batch file to perform proper cleanup. Compilation Project was created alongside Visual Studio 2013. You should in...

Dirhunt V0.6.0 - Uncovering Spider Web Directories Without Bruteforce

Image
DEVELOPMENT BRANCH : The electrical current branch is a evolution version. Go to the stable issue past times clicking on the principal branch . Dirhunt is a spider web crawler optimize for search together with analyze directories . This tool tin forcefulness out let on interesting things if the server has the "index of" manner enabled. Dirhunt is also useful if the directory listing is non enabled. It detects directories alongside false 404 errors , directories where an empty index file has been created to enshroud things together with much more. $ dirhunt http://website.com/ Dirhunt does non operate beast force. But neither is it only a crawler . This tool is faster than others because it minimizes requests to the server. Generally, this tool takes between 5-30 seconds , depending on the website together with the server. Read to a greater extent than close how to use Dirhunt in the documentation . Features Process one or multiple sites at a time. P...

Manticore - Symbolic Execution Tool For Analysis Of Binaries In Addition To Smart Contracts

Image
Manticore is a symbolic execution tool for analysis of binaries too smart contracts. Note: Beginning amongst version 0.2.0, Python 3.6+ is required. Features Input Generation : Manticore automatically generates inputs that trigger unique code paths Crash Discovery : Manticore discovers inputs that crash programs via retention security violations Execution Tracing : Manticore records an instruction-level line of execution for each generated input Programmatic Interface : Manticore exposes programmatic access to its analysis engine via a Python API Manticore tin plough over the sack analyze the next types of programs: Ethereum smart contracts (EVM bytecode) Linux ELF binaries (x86, x86_64 too ARMv7) Usage CLI Manticore has a command line interface which tin plough over the sack move used to easily symbolically execute a supported plan or smart contract. Analysis results volition move placed into a novel directory outset amongst mcore_ . Use the CLI to explore po...

Cms Scanner - Scan Wordpress, Drupal, Joomla, Vbulletin Websites For Safety Issues

Image
Scan Wordpress, Drupal, Joomla, vBulletin websites for Security issues. CMSScan provides a centralized Security Dashboard for CMS Security scans. It is powered past times wpscan, droopescan, vbscan as well as joomscan. It supports both on involve as well as scheduled scans as well as has the might to sent electronic mail reports. Install # Requires ruby, ruby-dev, gem, python3 as well as git git clone https://github.com/ajinabraham/CMSScan.git cd CMSScan ./setup.sh Run ./run.sh Periodic Scans You tin perform periodic CMS scans alongside CMSScan. You must piece of work CMSScan server separately as well as configure the next earlier running the scheduler.py script. # SMTP SETTINGS SMTP_SERVER = '' FROM_EMAIL = '' TO_EMAIL = '' # SERVER SETTINGS SERVER = '' # SCAN SITES WORDPRESS_SITES = [] DRUPAL_SITES = [] JOOMLA_SITES = [] VBULLETIN_SITES = [] Add a cronjob crontab -e @weekly /usr/bin/python3 scheduler.py Docker Local docker...

Janusec Application Gateway - Tool Which Provides Waf, Cc Develop On Defense, Unified Spider Web Direction Portal, Someone Fundamental Protection, Spider Web Routing Together With Scalable Charge Balancing

Image
Janusec Application Gateway, an application safety solutions which provides WAF (Web Application Firewall), unified spider web direction portal, someone fundamental protection, spider web routing as well as scalable charge balancing. With Janusec, y'all tin ship away construct secure as well as scalable applications. Key Features WAF (Web Application Firewall), block SQL Injection, Cross-site Scripting, Sensitive Data Leakage, CC Attacks etc. Group Policy (Cooperation amongst Multiple Check Points) CAPTCHA support Unified Web Administration HTTPS support, No Agent Required. Certificate Protection amongst Private Key Encrypted Storage Scalable Architecture, Load Balance as well as Multiple Nodes Support Screenshots SQL Injection Screenshot Sensitive Data Leakage Screenshot Official Web Site https://www.janusec.com/ Detailed documentation is available at Janusec Application Gateway Documentation . Requirements PostgreSQL 9.3 9.6 or ten (Requi...

Trape V2.0 - People Tracker On The Internet: Osint Analysis In Addition To Inquiry Tool

Image
Trape is a OSINT analysis in addition to query tool, which allows people to rails in addition to execute intelligent social engineering attacks inwards existent time. It was created amongst the aim of teaching the footing how large Internet companies could obtain confidential information such every bit the condition of sessions of their websites or services in addition to command over their users through the browser, without them knowing, but It evolves amongst the aim of helping government organizations, companies in addition to researchers to rails the cybercriminals. At the commencement of the yr 2018 was presented at BlackHat Arsenal inwards Singapore : https://www.blackhat.com/asia-18/arsenal.html#jose-pino in addition to inwards multiple safety events worldwide. Some benefits LOCATOR OPTIMIZATION: Trace the path betwixt you lot in addition to the target you're tracking. Each fourth dimension you lot brand a move, the path volition survive updated, past t...

Cameradar V2.1.0 - Hacks Its Mode Into Rtsp Videosurveillance Cameras

Image
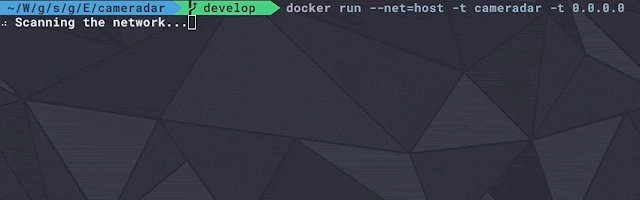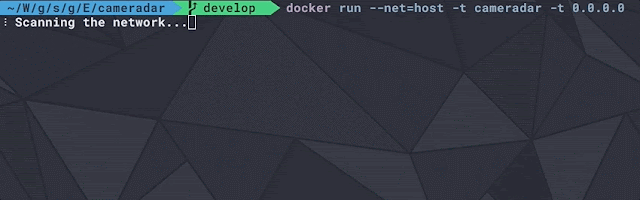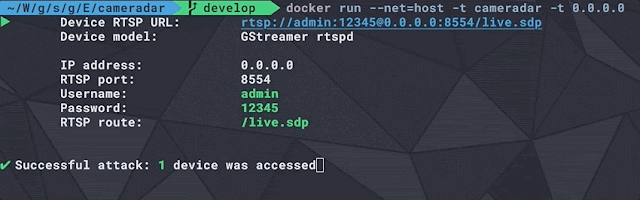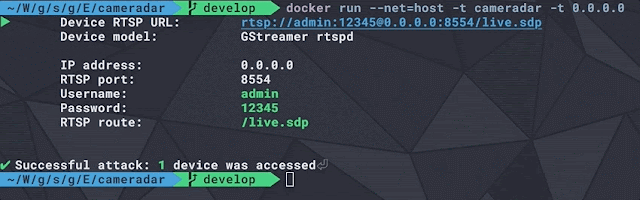
   An RTSP flow access tool that comes alongside its library Cameradar allows you lot to Detect opened upward RTSP hosts on whatever accessible target host Detect which device model is streaming Launch automated dictionary attacks to larn their stream route (e.g.: /live.sdp ) Launch automated lexicon attacks to larn the username in addition to password of the cameras Retrieve a consummate in addition to user-friendly study of the results Docker Image for Cameradar Install docker on your machine, in addition to run the next command: docker run -t ullaakut/cameradar -t <target> <other command-line options> See command-line options . e.g.: docker run -t ullaakut/cameradar -t 192.168.100.0/24 -l volition scan the ports 554 in addition to 8554 of hosts on the 192.168.100.0/24 subnetwork in addition to laid on the discovered RTSP streams in addition to volition output debug logs. YOUR_TARGET tin hold out a subnet (e.g.: 172.16.100.0/24 )...

Dawnscanner - Dawn Is A Static Analysis Safety Scanner For Cherry-Red Written Spider Web Applications (Sinatra, Padrino In Addition To Ror Frameworks)

Image
dawnscanner is a source code scanner designed to review your ruby code for safety issues. dawnscanner is able to scan manifestly ruby scripts (e.g. command trace applications) but all its features are unleashed when dealing amongst spider web applications source code. dawnscanner is able to scan major MVC (Model View Controller) frameworks, out of the box: Ruby on Rails Sinatra Padrino Quick update from November, 2018 As yous tin run into dawnscanner is on concord since to a greater extent than together with thus an year. Sorry for that. It's life. I was overwhelmed past times tons of materials together with I dedicated gratis fourth dimension to Offensive Security certifications. True to hold out told, I'm starting OSCE journeying truly soon. The dawnscanner projection volition hold out updated shortly amongst novel safety checks together with kickstarted again. Paolo dawnscanner version 1.6.6 has 235 safety checks loaded inwards its cognition base. M...