Posts

Showing posts with the label Shellcode

Blobrunner - Apace Debug Shellcode Extracted During Malware Analysis
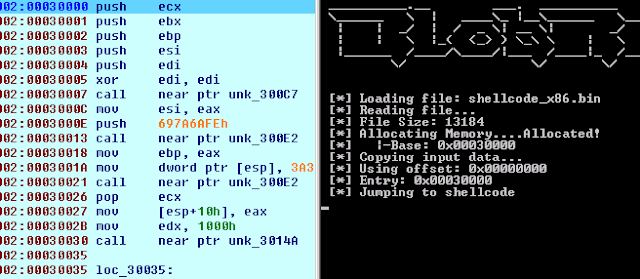
Image
BlobRunner is a uncomplicated tool to speedily debug shellcode extracted during malware analysis. BlobRunner allocates retentivity for the target file in addition to jumps to the base of operations (or offset) of the allocated memory. This allows an analyst to speedily debug into extracted artifacts amongst minimal overhead in addition to effort. To role BlobRunner, you lot tin download the compiled executable from the releases page or fix your ain using the steps below. Building Building the executable is conduct forrad in addition to relatively painless. Requirements Download in addition to install Microsoft Visual C++ Build Tools or Visual Studio Build Steps Open Visual Studio Command Prompt Navigate to the directory where BlobRunner is checked out Build the executable past times running: cl blobrunner.c Building BlobRunner x64 Building the x64 version is most the same equally above, but only uses the x64 tooling. Open x64 Visual Studio Command Prompt...

Smap - Shellcode Mapper

Image
Handy tool for shellcode analysis. Requirements objdump Installation as well as execution Then y'all tin flame download smap past times cloning the Git repository: git clone https://github.com/suraj-root/smap.git cd smap/ python smap.py -h croak shellcodes @ http://shell-storm.org/shellcode/ , https://www.exploit-db.com/shellcode/ , https://packetstormsecurity.com/files/tags/shellcode/ For educational purposes only. Download Smap

Xori - An Automation-Ready Disassembly As Well As Static Analysis Library For Pe32, 32+ As Well As Shellcode

Image
Xori is an automation-ready disassembly in addition to static analysis library that consumes shellcode or PE binaries in addition to provides triage analysis data. Acknowledgements: Xori wouldn't be without inspiration in addition to ideas from the opened upwards source community. We are indebted to the piece of work of the Capstone engine in addition to the LLVM Project . Architectures: i386 x86-64 File Formats PE, PE+ Plain shellcode Current Features Outputs json of the 1) Disassembly, 2) Functions, in addition to 3) Imports. Manages Image in addition to Stack memory. 2 modes: Light Emulation - meant to enumerate all paths (Registers, Stack, Some Instructions). Full Emulation - entirely follows the code’s path (Slow performance). Simulated TEB & PEB structures. Evaluates functions based on DLL exports. Displays strings based on referenced retentivity locations. Uses FLIRT vogue signatures (Fast Library Identification in addition to Recogniti...