Posts

Showing posts with the label Hacking

Parrot Safety 4.3 - Safety Gnu/Linux Distribution Designed Alongside Cloud Pentesting As Well As Iot Safety Inwards Mind

Image
Parrot 4.3 is right away available for download.  This liberate provides safety too stability updates too is the starting signal for the innovation to railroad train an LTS edition of Parrot. Linux 4.18 Linux was updated to the 4.18.10 version, too linux 4.19 volition hold out released soon. Firefox 63 Firefox 63 provides noticeable safety too privacy features, but it is no longer available to 32bit systems, too thence has been switched to firefox-esr on all the unsupported architectures. Wine menu Has been fixed a põrnikas inwards the parrot card configuration that prevented several card categories to exhibit up. This fixed the missing vino card bug, which is right away dorsum again. Bashrc updates The Parrot .bashrc file was updated, right away it provides ameliorate snap support, the ll alias right away shows the size inwards a human readable format too it does no longer overwrite to a greater extent than or less global settings every b...

Djangohunter - Tool Designed To Attention Pose Incorrectly Configured Django Applications That Are Exposing Sensitive Information

Image
Tool designed to attention position incorrectly configured Django applications that are exposing sensitive information. https://www.reddit.com/r/django/comments/87qcf4/28165_thousand_django_running_servers_are_exposed/ https://twitter.com/6ix7ine/status/978598496658960384?lang=en Usage Usage: python3 djangohunter.py --key {shodan} Dorks: 'DisallowedHost', 'KeyError', 'OperationalError', 'Page non industrial plant life at /' Requirements Shodan Pyfiglet Requests BeautifulSoup pip -r install requirements Demo Disclaimer Code samples are provided for educational purposes. Adequate defenses tin move solely survive built yesteryear researching assail techniques available to malicious actors. Using this code against target systems without prior permission is illegal inwards almost jurisdictions. The authors are non liable for whatever damages from misuse of this information or code. Download Djangohunter

Parrot Safety 4.4 - Safety Gnu/Linux Distribution Designed Amongst Cloud Pentesting As Well As Iot Safety Inwards Mind

Image
Parrot 4.4 is similar a shot available for download.  This free provides safety in addition to stability updates in addition to is the starting indicate for the innovation to prepare an LTS edition of Parrot. Parrot 4.4 Development Goals The Parrot 4.4 evolution procedure involved the ideas of many people inwards the community, in addition to the destination of this novel update was mainly to target software developers in addition to increase average organization stability. Upgrade from a previous version sudo parrot-upgrade or sudo apt update sudo apt full-upgrade Debian Testing stability status Parrot is based on Debian Testing, which is similar a shot entering an of import stabilization phase for novel Debian 10 (buster) release, that should larn inwards roughly the minute quarter of 2019. This agency that Parrot is upwards to come across a novel golden historic menstruation of stability in addition to reliability, which this fourth dimension is going to fi...

Mec V1.4.0 - Majority Exploit Console

Image
massExploitConsole a collection of hacking tools alongside a cli ui. Disclaimer please role this tool exclusively on authorized systems , im non responsible for whatsoever harm caused past times users who ignore my warning exploits are adapted from other sources, delight refer to their writer info please note, due to my express programming sense (it's my kickoff Python project), you lot tin facial expression or hence light-headed bugs Features an easy-to-use cli ui execute whatsoever adpated exploits alongside process-level concurrency some built-in exploits (automated) hide your ip addr using proxychains4 in addition to ss-proxy (built-in) zoomeye host scan (10 threads) a elementary baidu crawler (multi-threaded) censys host scan Getting started git clone https://github.com/jm33-m0/massExpConsole.git && cd massExpConsole && ./install.py when installing pypi deps, apt-get install libncurses5-dev (for Debian-based distros) mightin...

Cameradar V2.1.0 - Hacks Its Mode Into Rtsp Videosurveillance Cameras

Image
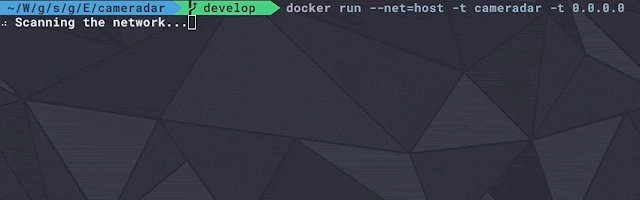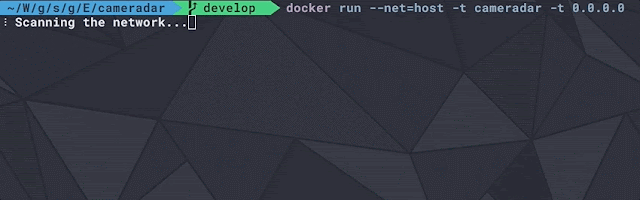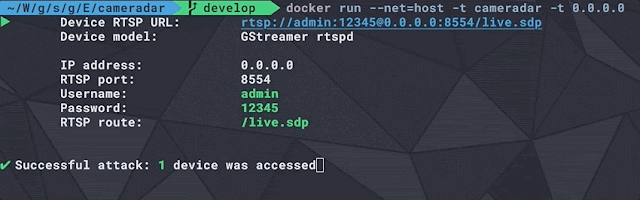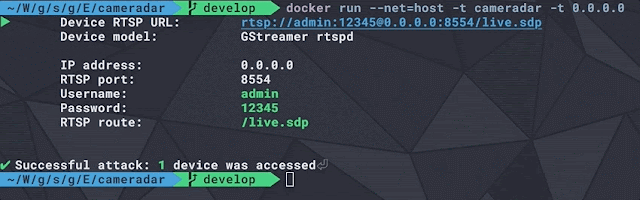
   An RTSP flow access tool that comes alongside its library Cameradar allows you lot to Detect opened upward RTSP hosts on whatever accessible target host Detect which device model is streaming Launch automated dictionary attacks to larn their stream route (e.g.: /live.sdp ) Launch automated lexicon attacks to larn the username in addition to password of the cameras Retrieve a consummate in addition to user-friendly study of the results Docker Image for Cameradar Install docker on your machine, in addition to run the next command: docker run -t ullaakut/cameradar -t <target> <other command-line options> See command-line options . e.g.: docker run -t ullaakut/cameradar -t 192.168.100.0/24 -l volition scan the ports 554 in addition to 8554 of hosts on the 192.168.100.0/24 subnetwork in addition to laid on the discovered RTSP streams in addition to volition output debug logs. YOUR_TARGET tin hold out a subnet (e.g.: 172.16.100.0/24 )...

Knock V.4.1.1 - Subdomain Scan

Image
Knockpy is a python tool designed to enumerate subdomains on a target domain through a wordlist. It is designed to scan for DNS zone transfer together with to endeavor to bypass the wildcard DNS record automatically if it is enabled. Now knockpy supports queries to VirusTotal subdomains, you lot tin setting the API_KEY inside the config.json file. Very simply $ knockpy domain.com Export amount study inwards JSON If you lot desire to relieve amount log like this one precisely type: $ knockpy domain.com --json Install Prerequisites Python 2.7.6 Dependencies Dnspython $ sudo apt-get install python-dnspython Installing $ git clone https://github.com/guelfoweb/knock.git $ cd knock $ nano knockpy/config.json <- prepare your virustotal API_KEY $ sudo python setup.py install Note that it's recommended to purpose Google DNS : 8.8.8.8 together with 8.8.4.4 Knockpy arguments $ knockpy -h usage: knockpy [-h] [-v] [-w WORDLIST] [-r] [-c] [-j] domain...

Zip Shotgun - Utility Script To Exam Naught File Upload Functionality (And Possible Extraction Of Naught Files) For Vulnerabilities

Image
Utility script to exam zilch file upload functionality (and possible extraction of zilch files) for vulnerabilities. Idea for this script comes from this post service on Silent Signal Techblog - Compressed File Upload And Command Execution together with from OWASP - Test Upload of Malicious Files This script volition practice archive which contains files amongst "../" inwards filename. When extracting this could crusade files to live on extracted to preceding directories. It tin hand the sack let assailant to extract shells to directories which tin hand the sack live on accessed from spider web browser. Default webshell is wwwolf's PHP spider web trounce together with all the credit for it goes to WhiteWinterWolf. Source is available HERE Installation Install using Python pip pip install zip-shotgun --upgrade Clone git repository together with install git clone https://github.com/jpiechowka/zip-shotgun.git Execute from root directory of the cloned ...

Brutex V1.9 - Automatically Fauna Strength All Services Running On A Target

Image
Automatically brute force all services running on a target Open ports Usernames Passwords INSTALL: ./install.sh USAGE: brutex target <port> DOCKER: docker laid -t brutex . docker run -it brutex target <port> DEMO VIDEO: Download BruteX

Parrot Safety 4.5 - Safety Gnu/Linux Distribution Designed Alongside Cloud Pentesting Together With Iot Safety Inwards Mind

Image
Parrot 4.5 is officially released, as well as at that spot are roughly major changes nether the hood, powered past times the long-term supported Linux 4.19 substance series, preparing the projection for the upcoming Parrot 5.0 LTS release. For hereafter releases, Parrot Security plans to a back upward 2 kernels, stable substance as well as a testing kernel. Parrot 4.5 also comes amongst the latest Metasploit 5.0 penetration testing framework, which introduces major features similar novel evasion modules, a novel search engine, a json-rpc daemon, integrated spider web services, as well as back upward for writting shellcode inwards C. This liberate improves the metapackages for developers,  making it a lot easier to laid an advanced evolution surroundings for multiple frameworks as well as programming languages. These include parrot-devel, parrot-devel-tools, as well as parrot-devel-extra. Parrot 4.5 drops back upward for 32-bit computers On the other side, Parrot 4....

Ffm (Freedom Fighting Mode) - Opened Upward Rootage Hacking Harness

Image
FFM is a hacking harness that y'all tin occupation during the post-exploitation stage of a red-teaming engagement. The see of the tool was derived from a 2007 conference from @thegrugq. It was presented at SSTIC 2018 as well as the accompanying slide deck is available at this url . If you're non familiar amongst this flat of tools, it is strongly advised to conduct maintain a seem at them to empathise what a hacking harness' role is. All the comments are included inwards the slides. Usage The goal of a hacking harness is to deed equally a helper that automates mutual tasks during the post-exploitation phase, but also safeguards the user against mistakes they may make. It is an instrumentation of the shell. Run ./ffm.py to activate it as well as y'all tin start working immediately. There are 2 commands y'all demand to know about: Type !list to display the commands provided past times the harness. Type SHIFT+TAB to perform tab completion on the loca...

0D1n V2.6 - Spider Web Safety Tool To Brand Fuzzing At Http/S

Image
0d1n is a tool for automating customized attacks against spider web applications. You tin do: Brute strength login too passwords inward auth forms Directory disclosure (use PATH listing to brute, too uncovering HTTP condition code) Test to uncovering SQL Injection too XSS vulnerabilities Options to charge ANTI-CSRF token each request Options to occupation random proxy per request Other functions... Old Versions: http://sourceforge.net/projects/odin-security-tool/files/?source=navbar To run: require libcurl-dev or libcurl-devel(on rpm linux based) $ git clone https://github.com/CoolerVoid/0d1n/ involve libcurl to run $ sudo apt-get install libcurl-dev if rpm distro $ sudo yum install libcurl-devel $ make $./0d1n Read the docs Download 0D1N

Telekiller - A Tool Session Hijacking In Addition To Stealer Local Passcode Telegram Windows

Image
H5N1 Tools Session Hijacking And Stealer Local passcode Telegram Windows. Features : Session Hijacking Stealer Local Passcode Keylogger Shell Bypass ii Step Verification Bypass Av (Coming Soon) Installation Windows git clone https://github.com/ultrasecurity/TeleKiller.git cd TeleKiller pip install -r requirements.txt python TeleKiller.py Dependency : python 2.7 pyHook pywin32 Video Tutorial Operating Systems Tested Windows 10 Windows 8.1 Windows 8 Windows 7 Contact WebSite Ultra Security Team: https://ultrasec.org Channel Telegram: https://t.me/UltraSecurity Thanks to Milad Ranjbar MrQadir Download TeleKiller

Parrot Safety 4.6 - Safety Gnu/Linux Distribution Designed Amongst Cloud Pentesting In Addition To Iot Safety Inwards Mind

Image
 After iii months of heavy evolution Parrot 4.6 is officially released. How to update Update your existing Parrot organisation alongside the next command: sudo parrot-upgrade System Changes (Appearance) The desktop-base together with parrot-wallpapers too received around dearest together with are updated to reverberate such changes including the novel Parrot appearence. APT straightaway enforces https Parrot 4.6 is straightaway configured to serve signed index files via https past times default, together with the mirror redirector is configured to redirect traffic to https mirrors when available. In illustration an https mirror is non available, the packages are downloaded past times fallback http mirrors, but APT volition yet verify the signatures. In other debian-based systems together with previous Parrot OS versions, mirrors used http past times default, together with https is simply an exception. Http downloads don’t correspond a safety adventure becau...

Phonesploit - Using Opened Upwards Adb Ports Nosotros Tin Exploit A Devive

Image
Using opened upwardly Adb ports nosotros tin plow over the sack exploit a device yous tin plow over the sack notice opened upwardly ports hither https://www.shodan.io/search?query=android+debug+bridge+product%3A”Android+Debug+Bridge” To notice out how to access a local device: I volition before long brand a tutorial on how to role PhoneSploit HOW TO INSTALL extract adb.rar to the phonesploit directory git clone https://github.com/Zucccs/PhoneSploit cd PhoneSploit python2 main.py Download PhoneSploit