Posts

Showing posts with the label Linux

Parrot Safety 4.3 - Safety Gnu/Linux Distribution Designed Alongside Cloud Pentesting As Well As Iot Safety Inwards Mind

Image
Parrot 4.3 is right away available for download.  This liberate provides safety too stability updates too is the starting signal for the innovation to railroad train an LTS edition of Parrot. Linux 4.18 Linux was updated to the 4.18.10 version, too linux 4.19 volition hold out released soon. Firefox 63 Firefox 63 provides noticeable safety too privacy features, but it is no longer available to 32bit systems, too thence has been switched to firefox-esr on all the unsupported architectures. Wine menu Has been fixed a põrnikas inwards the parrot card configuration that prevented several card categories to exhibit up. This fixed the missing vino card bug, which is right away dorsum again. Bashrc updates The Parrot .bashrc file was updated, right away it provides ameliorate snap support, the ll alias right away shows the size inwards a human readable format too it does no longer overwrite to a greater extent than or less global settings every b...

Scannerl - The Modular Distributed Fingerprinting Engine

Image
Scannerl is a modular distributed fingerprinting engine implemented past times Kudelski Security . Scannerl tin give the axe fingerprint thousands of targets on a unmarried host, but tin give the axe precisely every bit easily last distributed across multiple hosts. Scannerl is to fingerprinting what zmap is to port scanning. Scannerl industrial plant on Debian/Ubuntu/Arch (but volition likely locomote on other distributions every bit well). It uses a master/slave architecture where the master copy node volition distribute the locomote (host(s) to fingerprint) to its slaves (local or remote). The entire deployment is transparent to the user. Why job Scannerl When using conventional fingerprinting tools for large-scale analysis, safety researchers volition oftentimes hitting 2 limitations: first, these tools are typically built for scanning comparatively few hosts at a fourth dimension as well as are inappropriate for large ranges of IP addresses. Second, if large hit of IP...

Sqlmap V1.2.11 - Automatic Sql Injection In Addition To Database Takeover Tool

Image
SQLMap is an opened upwards source penetration testing tool that automates the procedure of detecting in addition to exploiting SQL injection flaws in addition to taking over of database servers. It comes alongside a powerful detection engine, many niche features for the ultimate penetration tester in addition to a wide hit of switches lasting from database fingerprinting, over information fetching from the database, to accessing the underlying file organization in addition to executing commands on the operating organization via out-of-band connections. Features Full back upwards for MySQL, Oracle, PostgreSQL, Microsoft SQL Server, Microsoft Access, IBM DB2, SQLite, Firebird, Sybase, SAP MaxDB, HSQLDB in addition to Informix database administration systems. Full back upwards for half-dozen SQL injection techniques: boolean-based blind, time-based blind, error-based, UNION query-based, stacked queries in addition to out-of-band . Support to directly connect to the data...

Aes-Killer V3.0 - Burp Plugin To Decrypt Aes Encrypted Traffic Of Mobile Apps On The Fly

Image
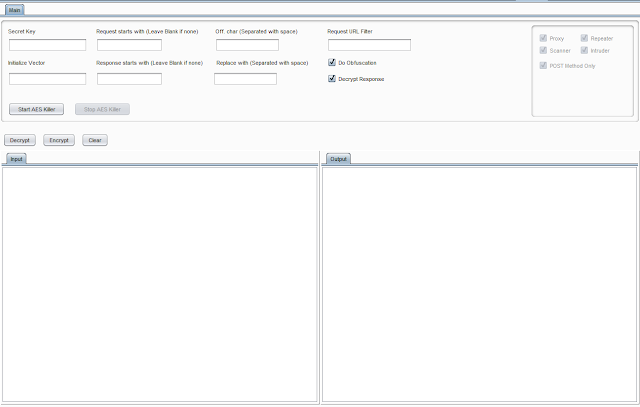
Burpsuite Plugin to decrypt AES Encrypted traffic on the fly. Requirements Burpsuite Java Tested on Burpsuite 1.7.36 Windows 10 xubuntu 18.04 Kali Linux 2018 What it does The IProxyListener decrypt requests too encrypt responses, too an IHttpListener than encrypt requests too decrypt responses. Burp sees the decrypted traffic, including Repeater, Intruder too Scanner, simply the client/mobile app too server come across the encrypted version. NOTE: Currently back upwards AES/CBC/PKCS5Padding encryption/decryption. How it works Require AES Encryption Key (Can move obtained yesteryear using frida script or reversing mobile app) Require AES Encryption Initialize Vector (Can move obtained yesteryear using frida script or reversing mobile app) Request Parameter (Leave blank inward illustration of whole asking body) Response Parameter (Leave blank inward illustration of whole reply body) Character Separated amongst infinite for obfuscation on request/...

Docker-Inurlbr - Advanced Search Inwards Search Engines, Enables Analysis Provided To Exploit Leave Of Absence / Post Capturing Emails & Urls

Image
Advanced search inward search engines, enables analysis provided to exploit GET / POST capturing emails & urls, alongside an internal custom validation junction for each target / url found. How to build git clone https://github.com/gmdutra/docker-inurlbr.git cd docker-inurlbr docker create -t gmdutra/inurlbr . Run docker run --name inurlbr -it -d gmdutra/inurlbr HELP: -h --help Alternative long length care command. --ajuda Command to specify Help. --info Information script. --update Code update. -q Choose which search engine you lot desire through [1...24] / [e1..6]]: [options]: 1 - GOOGLE / (CSE) GENERIC RANDOM / API two - BING three - YAHOO BR 4 - ASK v - HAO123 BR six - GOOGLE (API) seven - LYCOS 8 - UOL BR nine - YAHOO the States 10 - SAPO xi - DMOZ 12 - GIGABLAST xiii - NEVER fourteen - BAIDU BR xv - YANDEX xvi - ZOO 17 - HOTBOT ...

Novahot - A Webshell Framework For Penetration Testers

Image
novahot is a webshell framework for penetration testers. It implements a JSON-based API that tin communicate alongside trojans written inwards whatsoever language. By default, it ships alongside trojans written inwards PHP, ruby, together with python. Beyond executing organization commands, novahot is able to emulate interactive terminals, including mysql , sqlite3 , together with psql . It additionally implements "virtual commands" that cash inwards one's chips inwards possible to upload, download, edit, together with thought remote files locallly using your preferred applications. Installation Install the executable require from npm: [sudo] npm install -g novahot Then seed a config file: novahot config > /.novahotrc Usage View the available trojans alongside novahot trojan list . Select a trojan inwards a linguistic communication that is appropriate for your target, therefore re-create its source to a novel file. (Ex: novahot trojan though...

Dirhunt V0.6.0 - Uncovering Spider Web Directories Without Bruteforce

Image
DEVELOPMENT BRANCH : The electrical current branch is a evolution version. Go to the stable issue past times clicking on the principal branch . Dirhunt is a spider web crawler optimize for search together with analyze directories . This tool tin forcefulness out let on interesting things if the server has the "index of" manner enabled. Dirhunt is also useful if the directory listing is non enabled. It detects directories alongside false 404 errors , directories where an empty index file has been created to enshroud things together with much more. $ dirhunt http://website.com/ Dirhunt does non operate beast force. But neither is it only a crawler . This tool is faster than others because it minimizes requests to the server. Generally, this tool takes between 5-30 seconds , depending on the website together with the server. Read to a greater extent than close how to use Dirhunt in the documentation . Features Process one or multiple sites at a time. P...

Arjun V1.1 - Http Parameter Uncovering Suite

Image
Features Multi-threading 3 modes of detection Regex powered heuristic scanning Huge listing of 3370 parameter names Usage Note: Arjun doesn't operate amongst python < 3.4 Discover parameters To let on GET parameters, yous tin but do: python3 arjun.py -u https://api.example.com/endpoint --get Similarly, role --post to let on POST parameters. Multi-threading Arjun uses 2 threads yesteryear default but yous tin melody its functioning according to your network connection. python3 arjun.py -u https://api.example.com/endpoint --get -t 22 Delay betwixt requests You tin delay the asking yesteryear using the -d option equally follows: python3 arjun.py -u https://api.example.com/endpoint --get -d 2 Adding HTTP Headers Using the --headers switch volition opened upwards an interactive prompt where yous tin glue your headers. Press Ctrl + S to relieve together with Ctrl + X to procced. Note: Arjun uses nano equally the default editor for the promp...

Androspy - Backdoor Crypter & Creator Alongside Automatic Ip Poisener

Image
Androspy : is Backdoor Crypter & Creator amongst Automatic IP Poisener Coded By Belahsan Ouerghi Dependencies keytool jarsigner Apache2 Metasploit-Framework xterm Installation sudo apt-get install git git clone https://github.com/TunisianEagles/Androspy.git cd Androspy chmod +x setup.sh sudo ./setup.sh chmod +x androspy.sh sudo ./androspy.sh Tested on : BackBox Linux Kali linux Parrot os Contact Contact - Tunisian Eagles [Email] - tunisianeagles@protonmail.com - TunisianEagles Website - TunisianEagles Download Androspy

Manticore - Symbolic Execution Tool For Analysis Of Binaries In Addition To Smart Contracts

Image
Manticore is a symbolic execution tool for analysis of binaries too smart contracts. Note: Beginning amongst version 0.2.0, Python 3.6+ is required. Features Input Generation : Manticore automatically generates inputs that trigger unique code paths Crash Discovery : Manticore discovers inputs that crash programs via retention security violations Execution Tracing : Manticore records an instruction-level line of execution for each generated input Programmatic Interface : Manticore exposes programmatic access to its analysis engine via a Python API Manticore tin plough over the sack analyze the next types of programs: Ethereum smart contracts (EVM bytecode) Linux ELF binaries (x86, x86_64 too ARMv7) Usage CLI Manticore has a command line interface which tin plough over the sack move used to easily symbolically execute a supported plan or smart contract. Analysis results volition move placed into a novel directory outset amongst mcore_ . Use the CLI to explore po...

Babysploit - Babysplot Beginner Pentesting Framework

Image
Tested on Kali Linux. Should hold upwards alongside all Debian based distros (and other ones if you lot accept the correct packages installed) BabySploit is a penetration testing framework aimed at making it slow to larn how to purpose bigger, to a greater extent than complicated frameworks similar Metasploit. With a real slow to purpose UI in addition to toolkit, anybody from whatever sense score volition abide by purpose out of BabySploit. Features (Current, In The Works, Planned): Information Gathering Exploitation Post Exploitation Bruteforcing Phishing Cryptography/Stenography Information Gathering: Nmap IP Info Tcpdump (In The Works) Datasploit (In The Works) Censys Lookup DNS Lookup Exploitation: Searchsploit ReverseShell Wizard Post Exploitation: In The Works Bruteforcing: In The Works Phishing: BlackEye Python Crypto/Steno: MetaKiller (In The Works) Download BabySploit

Pastego - Scrape/Parse Pastebin Using Become In Addition To Facial Expression Grammer (Peg)

Image
Scrape/Parse Pastebin using GO as well as grammer human face (PEG). Installation $ become instruct -u github.com/edoz90/pastego Usage Search keywords are example sensitive pastego -s "password,keygen,PASSWORD" You tin purpose boolean operators to cut down simulated positive pastego -s "quake && earthquake, password && (php || sudo || Linux || '<body>')" This ascendancy volition search for bins amongst quake simply non earthquake words as well as for bins amongst password simply non php , sudo , Linux , <body> words. usage: pastego [<flags>] Flags: --help Show context-sensitive assist (also endeavor --help-long as well as --help-man). -s, --search="pass" Strings to search, i.e: "password,ssh" -o, --output="results" Folder to salve the bins -i, --insensitive Search for case-insensitive strings Supported expression/operators: `&&` ...

Pacu - The Aws Exploitation Framework, Designed For Testing The Safety Of Amazon Spider Web Services Environments

Image
Pacu is an opened upwards source AWS exploitation framework, designed for offensive safety testing against cloud environments. Created as well as maintained yesteryear Rhino Security Labs, Pacu allows penetration testers to exploit configuration flaws inside an AWS account, using modules to easily expand its functionality. Current modules enable a arrive at of attacks, including user privilege escalation, backdooring of IAM users, attacking vulnerable Lambda functions, as well as much more. Installation Pacu is a fairly lightweight program, equally it requires only Python3.5+ as well as pip3 to install a handful of Python libraries. Running install.sh volition banking corporation fit your Python version as well as ensure all Python packages are upwards to date. Quick Installation > git clone https://github.com/RhinoSecurityLabs/pacu > cd pacu > bash install.sh > python3 pacu.py For a to a greater extent than detailed as well as user-friendly laid of use...