Posts

Showing posts with the label Pcap

Isip - Interactive Drink Toolkit For Bundle Manipulations, Sniffing, Human Inwards The Meat Attacks, Fuzzing, Simulating Of Dos Attacks
Image
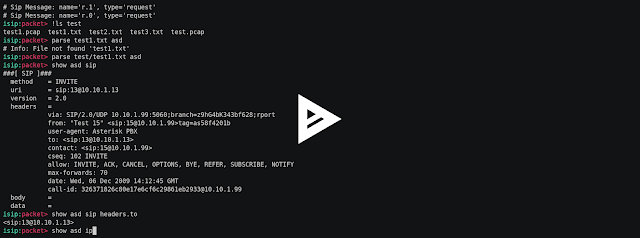
Interactive gulp toolkit for parcel manipulations, sniffing, man inwards the middle attacks, fuzzing, simulating of dos attacks. Video Setup git clone https://github.com/halitalptekin/isip.git cd isip pip install -r requirements.txt Usage Packet manipulation tools are inwards packet cmd loop. First start, you lot are inwards the main cmd loop. isip:main> parcel isip:packet> Create a novel gulp parcel amongst new command. If you lot don't write name, isip practise the parcel named yesteryear message-{id} . isip:packet> novel isip:packet> novel r1 List the all created gulp packets amongst list command. isip:packet> list Show properties of packets amongst show command. You tin type ip , udp or sip amongst show command. isip:packet> present message-1 isip:packet> present message-1 ip isip:packet> present message-1 udp isip:packet> present message-1 gulp isip:packet> present message-1 ip src isip:packet> pre...
Sniffair - A Framework For Wireless Pentesting

Image
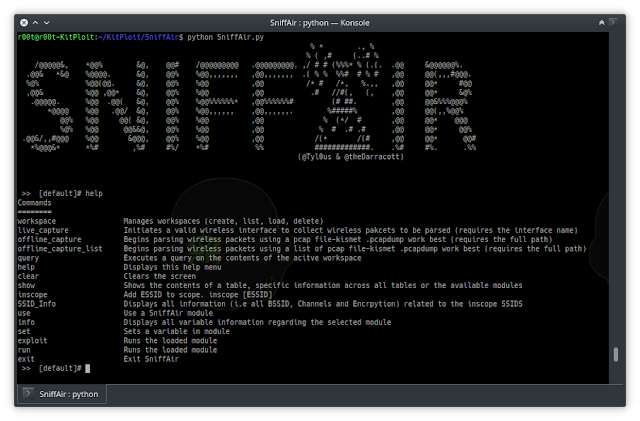
SniffAir is an open-source wireless safety framework which provides the mightiness to easily parse passively collected wireless information every bit good every bit launch sophisticated wireless attacks. SniffAir takes aid of the hassle associated alongside managing large or multiple pcap files land thoroughly cross-examining as well as analyzing the traffic, looking for potential safety flaws. Along alongside the prebuilt queries, SniffAir allows users to exercise custom queries for analyzing the wireless information stored inward the backend SQL database. SniffAir is built on the concept of using these queries to extract information for wireless penetration test reports. The information tin every bit good survive leveraged inward setting upwards sophisticated wireless attacks included inward SniffAir every bit modules. SniffAir is developed past times @Tyl0us as well as @theDarracott Install SniffAir was developed alongside Python version 2.7 Tested as well as supported o...

Tcpreplay - Pcap Editing Together With Replay Tools For *Nix Together With Windows

Image
Tcpreplay is a suite of GPLv3 licensed utilities for UNIX (and Win32 nether Cygwin ) operating systems for editing as well as replaying network traffic which was previously captured past times tools similar tcpdump as well as Ethereal / Wireshark . It allows y'all to separate traffic equally customer or server, rewrite Layer 2, iii as well as four packets as well as in conclusion replay the traffic dorsum onto the network as well as through other devices such equally switches, routers, firewalls, NIDS as well as IPS's. Tcpreplay supports both unmarried as well as dual NIC modes for testing both sniffing as well as in-line devices. Tcpreplay is used past times numerous firewall, IDS, IPS, NetFlow as well as other networking vendors, enterprises, universities, labs as well as opened upwardly source projects. If your organization uses Tcpreplay, delight allow us know who y'all are as well as what y'all purpose it for as well as so that I tin proceed to add togethe...

Malcom - Malware Communications Analyzer

Image
Malcom is a tool designed to analyze a system's network communication using graphical representations of network traffic, as well as cross-reference them amongst known malware sources. This comes handy when analyzing how sure enough malware species endeavour to communicate amongst the exterior world. What is Malcom? Malcom tin flame assistance you: detect primal command as well as command (C&C) servers understand peer-to-peer networks observe DNS fast-flux infrastructures quickly create upwardly one's heed if a network artifact is 'known-bad' The aim of Malcom is to brand malware analysis as well as intel gathering faster past times providing a human-readable version of network traffic originating from a given host or network. Convert network traffic information to actionable intelligence faster. Check the wiki for a Quickstart amongst closed to dainty screenshots as well as a tutorial on how to add together your ain feeds . If yous demand closed...

Wifi-Pumpkin V0.8.7 - Framework For Rogue Wi-Fi Access Betoken Attack

Image
The WiFi-Pumpkin is a rogue AP framework to easily exercise these mistaken networks, all piece forwarding legitimate traffic to together with from the unsuspecting target. It comes stuffed amongst features, including rogue Wi-Fi access points, deauth attacks on customer APs, a probe request together with credentials monitor, transparent proxy, Windows update attack, phishing manager, ARP Poisoning, DNS Spoofing, Pumpkin-Proxy, together with ikon capture on the fly. moreover, the WiFi-Pumpkin is a rattling consummate framework for auditing Wi-Fi safety depository fiscal establishment jibe the listing of features is quite broad. Installation Python 2.7 git clone https://github.com/P0cL4bs/WiFi-Pumpkin.git cd WiFi-Pumpkin ./installer.sh --install or download .deb file to install sudo dpkg -i wifi-pumpkin-0.8.7-all.deb sudo apt-get -f install # strength install dependencies if non install normally refer to the wiki for Installation Features Rogue Wi-Fi Access Po...

Pfq - Functional Network Framework For Multi-Core Architectures

Image
PFQ is a functional framework designed for the Linux operating arrangement built for efficient packets capture/transmission (10G, 40G too beyond), in-kernel functional processing, kernel-bypass too packets steering across groups of sockets/end-points. It is highly optimized for multi-core architecture, equally good equally for network devices equipped amongst multiple hardware queues. Compliant amongst whatsoever NIC, it provides a script that generates accelerated network device drivers starting from the source code. PFQ enables the evolution of high-performance network applications, too it is shipped amongst a custom version of libpcap that accelerate too parallelize legacy applications. Besides, a pure functional linguistic communication designed for early on stages in-kernel package processing is included: pfq-lang. Pfq-Lang is inspired yesteryear Haskell too is intended to define applications that run on top of network device drivers. Through pfq-lang it is possible to ...

Joy - A Packet For Capturing As Well As Analyzing Network Menstruation Information As Well As Intraflow Data, For Network Research, Forensics, As Well As Safety Monitoring

Image
Joy is a BSD-licensed libpcap-based software bundle for extracting information features from alive network traffic or packet capture (pcap) files, using a flow-oriented model like to that of IPFIX or Netflow, too and then representing these information features inward JSON. It also contains analysis tools that tin travel applied to these information files. Joy tin travel used to explore information at scale, peculiarly safety too threat-relevant data. JSON is used inward social club to brand the output easily consumable past times information analysis tools. While the JSON output files are somewhat verbose, they are reasonably small, too they response good to compression. Joy tin travel configured to obtain intraflow data, that is, information too information virtually events that hap inside a network flow, including: the sequence of lengths too arrival times of IP packets, upwards to roughly configurable number of packets. the empirical probability distrib...

Termshark - A Final Ui For Tshark, Inspired Past Times Wireshark

Image
H5N1 finally user-interface for tshark, inspired past times Wireshark. If you're debugging on a remote automobile amongst a large pcap together with no wishing to scp it dorsum to your desktop, termshark tin give notice help! Features Read pcap files or sniff alive interfaces (where tshark is permitted). Inspect each packet using familiar Wireshark-inspired views Filter pcaps or alive captures using Wireshark's display filters Copy ranges of packets to the clipboard from the terminal Written inward Golang, compiles to a unmarried executable on each platform - downloads available for Linux (+termux), macOS, FreeBSD, together with Windows tshark has many to a greater extent than features that termshark doesn't bring out yet! See What's Next . Installation (FreeBSD) Termshark is inward the FreeBSD ports tree! To install the package, run: pkg install termshark To build/install the port, run: cd /usr/ports/net/termshark/ && brand insta...

Sniffglue - Secure Multithreaded Bundle Sniffer

Image
sniffglue is a network sniffer written inward rust. Network packets are parsed concurrently using a thread puddle to utilize all cpu cores. Project goals are that you lot tin sack run sniffglue securely on untrusted networks as well as that it must non crash when processing packets. The output should live equally useful equally possible yesteryear default. Usage sniffglue enp0s25 Installation There is an official packet available for archlinux: pacman -S sniffglue To construct from source, brand certain you lot accept libpcap as well as libseccomp installed, Debian/Ubuntu: libpcap-dev libseccomp-dev , Archlinux: libpcap libseccomp . cargo install sniffglue Protocols ethernet ipv4 ipv6 arp tcp udp icmp http tls dns dhcp cjdns eth beacons ssdp dropbox beacons 802.11 Docker You tin sack construct sniffglue equally a docker icon to debug container setups. The icon is currently close 11.1MB. It is recommended to force it to your ain registry. dock...

Pcapxray V2.5 - A Network Forensics Tool To Visualize A Parcel Capture Offline Equally A Network Diagram

Image
PcapXray is a Network Forensics Tool  To visualize a Packet Capture offline equally a Network Diagram including device identification, highlight of import communication too file extraction. PcapXray Design Specification Goal: Given a Pcap File, plot a network diagram displaying hosts inwards the network, network traffic, highlight of import traffic too Tor traffic equally good equally potential malicious traffic including information involved inwards the communication. Problem: Investigation of a Pcap file takes a long fourth dimension given initial glitch to commencement the investigation Faced past times every forensics investigator too anyone who is analyzing the network Location: https://github.com/Srinivas11789/PcapXray Solution: Speed upwards the investigation process Make a network diagram amongst the next features from a Pcap file Tool Highlights: Network Diagram – Summary Network Diagram of amount network Information: Web Traffic amon...