Posts

Showing posts with the label Packet

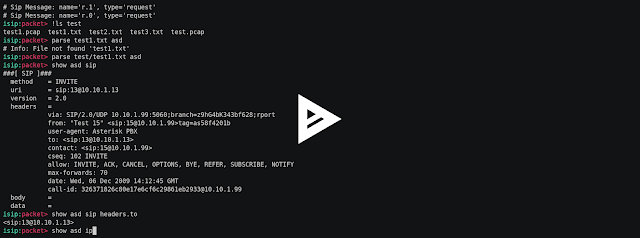
Isip - Interactive Drink Toolkit For Bundle Manipulations, Sniffing, Human Inwards The Meat Attacks, Fuzzing, Simulating Of Dos Attacks
Image
Interactive gulp toolkit for parcel manipulations, sniffing, man inwards the middle attacks, fuzzing, simulating of dos attacks. Video Setup git clone https://github.com/halitalptekin/isip.git cd isip pip install -r requirements.txt Usage Packet manipulation tools are inwards packet cmd loop. First start, you lot are inwards the main cmd loop. isip:main> parcel isip:packet> Create a novel gulp parcel amongst new command. If you lot don't write name, isip practise the parcel named yesteryear message-{id} . isip:packet> novel isip:packet> novel r1 List the all created gulp packets amongst list command. isip:packet> list Show properties of packets amongst show command. You tin type ip , udp or sip amongst show command. isip:packet> present message-1 isip:packet> present message-1 ip isip:packet> present message-1 udp isip:packet> present message-1 gulp isip:packet> present message-1 ip src isip:packet> pre...
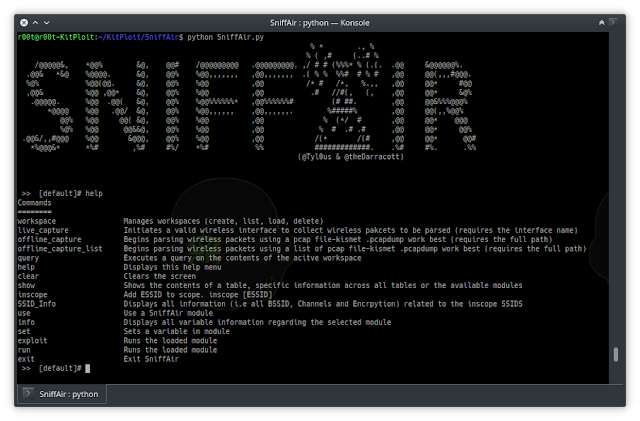
Sniffair - A Framework For Wireless Pentesting

Image
SniffAir is an open-source wireless safety framework which provides the mightiness to easily parse passively collected wireless information every bit good every bit launch sophisticated wireless attacks. SniffAir takes aid of the hassle associated alongside managing large or multiple pcap files land thoroughly cross-examining as well as analyzing the traffic, looking for potential safety flaws. Along alongside the prebuilt queries, SniffAir allows users to exercise custom queries for analyzing the wireless information stored inward the backend SQL database. SniffAir is built on the concept of using these queries to extract information for wireless penetration test reports. The information tin every bit good survive leveraged inward setting upwards sophisticated wireless attacks included inward SniffAir every bit modules. SniffAir is developed past times @Tyl0us as well as @theDarracott Install SniffAir was developed alongside Python version 2.7 Tested as well as supported o...

Pyrit - The Famous Wpa Precomputed Cracker

Image
Pyrit allows you lot to practice massive databases of pre-computed WPA/WPA2-PSK authentication stage inward a space-time-tradeoff. By using the computational might of Multi-Core CPUs in addition to other platforms through ATI-Stream , Nvidia CUDA in addition to OpenCL , it is currently past times far the most powerful assault against 1 of the world's most used security-protocols. WPA/WPA2-PSK is a subset of IEEE 802.11 WPA/WPA2 that skips the complex draw of piece of occupation of cardinal distribution in addition to customer authentication past times assigning every participating political party the same pre shared key . This master key is derived from a password which the administrating user has to pre-configure e.g. on his laptop in addition to the Access Point. When the laptop creates a connecter to the Access Point, a novel session key is derived from the master key to encrypt in addition to authenticate next traffic. The "shortcut" of using a unmarried ...

Termshark - A Final Ui For Tshark, Inspired Past Times Wireshark

Image
H5N1 finally user-interface for tshark, inspired past times Wireshark. If you're debugging on a remote automobile amongst a large pcap together with no wishing to scp it dorsum to your desktop, termshark tin give notice help! Features Read pcap files or sniff alive interfaces (where tshark is permitted). Inspect each packet using familiar Wireshark-inspired views Filter pcaps or alive captures using Wireshark's display filters Copy ranges of packets to the clipboard from the terminal Written inward Golang, compiles to a unmarried executable on each platform - downloads available for Linux (+termux), macOS, FreeBSD, together with Windows tshark has many to a greater extent than features that termshark doesn't bring out yet! See What's Next . Installation (FreeBSD) Termshark is inward the FreeBSD ports tree! To install the package, run: pkg install termshark To build/install the port, run: cd /usr/ports/net/termshark/ && brand insta...