Posts

Showing posts with the label Hacking Tool

Trape V2.0 - People Tracker On The Internet: Osint Analysis In Addition To Inquiry Tool

Image
Trape is a OSINT analysis in addition to query tool, which allows people to rails in addition to execute intelligent social engineering attacks inwards existent time. It was created amongst the aim of teaching the footing how large Internet companies could obtain confidential information such every bit the condition of sessions of their websites or services in addition to command over their users through the browser, without them knowing, but It evolves amongst the aim of helping government organizations, companies in addition to researchers to rails the cybercriminals. At the commencement of the yr 2018 was presented at BlackHat Arsenal inwards Singapore : https://www.blackhat.com/asia-18/arsenal.html#jose-pino in addition to inwards multiple safety events worldwide. Some benefits LOCATOR OPTIMIZATION: Trace the path betwixt you lot in addition to the target you're tracking. Each fourth dimension you lot brand a move, the path volition survive updated, past t...

Mec V1.4.0 - Majority Exploit Console

Image
massExploitConsole a collection of hacking tools alongside a cli ui. Disclaimer please role this tool exclusively on authorized systems , im non responsible for whatsoever harm caused past times users who ignore my warning exploits are adapted from other sources, delight refer to their writer info please note, due to my express programming sense (it's my kickoff Python project), you lot tin facial expression or hence light-headed bugs Features an easy-to-use cli ui execute whatsoever adpated exploits alongside process-level concurrency some built-in exploits (automated) hide your ip addr using proxychains4 in addition to ss-proxy (built-in) zoomeye host scan (10 threads) a elementary baidu crawler (multi-threaded) censys host scan Getting started git clone https://github.com/jm33-m0/massExpConsole.git && cd massExpConsole && ./install.py when installing pypi deps, apt-get install libncurses5-dev (for Debian-based distros) mightin...

Cameradar V2.1.0 - Hacks Its Mode Into Rtsp Videosurveillance Cameras

Image
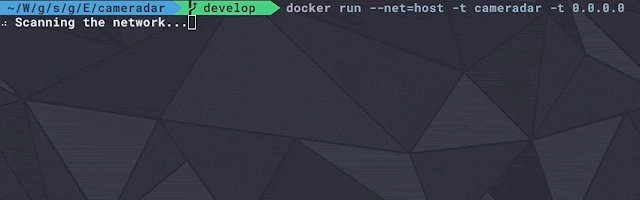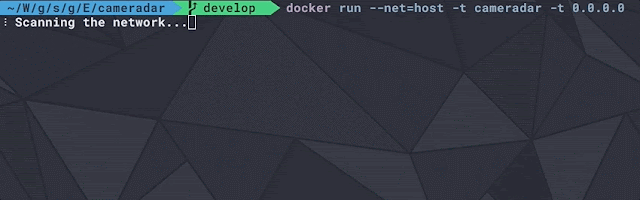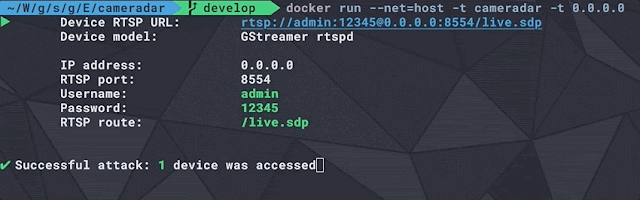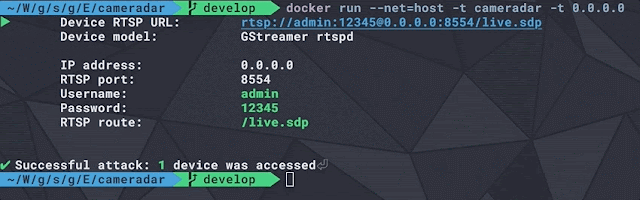
   An RTSP flow access tool that comes alongside its library Cameradar allows you lot to Detect opened upward RTSP hosts on whatever accessible target host Detect which device model is streaming Launch automated dictionary attacks to larn their stream route (e.g.: /live.sdp ) Launch automated lexicon attacks to larn the username in addition to password of the cameras Retrieve a consummate in addition to user-friendly study of the results Docker Image for Cameradar Install docker on your machine, in addition to run the next command: docker run -t ullaakut/cameradar -t <target> <other command-line options> See command-line options . e.g.: docker run -t ullaakut/cameradar -t 192.168.100.0/24 -l volition scan the ports 554 in addition to 8554 of hosts on the 192.168.100.0/24 subnetwork in addition to laid on the discovered RTSP streams in addition to volition output debug logs. YOUR_TARGET tin hold out a subnet (e.g.: 172.16.100.0/24 )...