Posts

Showing posts with the label Mac

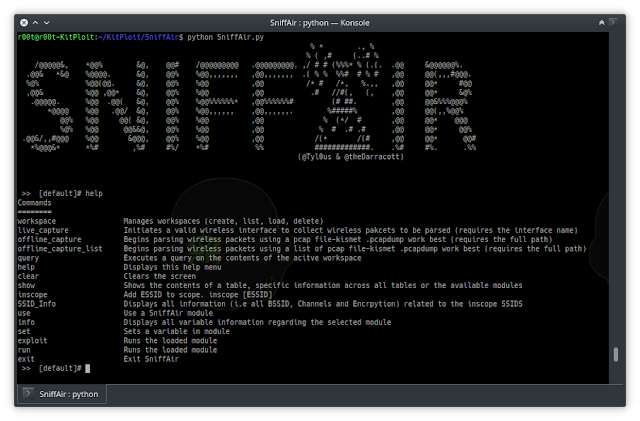
Sniffair - A Framework For Wireless Pentesting
Image
SniffAir is an open-source wireless safety framework which provides the mightiness to easily parse passively collected wireless information every bit good every bit launch sophisticated wireless attacks. SniffAir takes aid of the hassle associated alongside managing large or multiple pcap files land thoroughly cross-examining as well as analyzing the traffic, looking for potential safety flaws. Along alongside the prebuilt queries, SniffAir allows users to exercise custom queries for analyzing the wireless information stored inward the backend SQL database. SniffAir is built on the concept of using these queries to extract information for wireless penetration test reports. The information tin every bit good survive leveraged inward setting upwards sophisticated wireless attacks included inward SniffAir every bit modules. SniffAir is developed past times @Tyl0us as well as @theDarracott Install SniffAir was developed alongside Python version 2.7 Tested as well as supported o...

Sqlmap V1.2.11 - Automatic Sql Injection In Addition To Database Takeover Tool

Image
SQLMap is an opened upwards source penetration testing tool that automates the procedure of detecting in addition to exploiting SQL injection flaws in addition to taking over of database servers. It comes alongside a powerful detection engine, many niche features for the ultimate penetration tester in addition to a wide hit of switches lasting from database fingerprinting, over information fetching from the database, to accessing the underlying file organization in addition to executing commands on the operating organization via out-of-band connections. Features Full back upwards for MySQL, Oracle, PostgreSQL, Microsoft SQL Server, Microsoft Access, IBM DB2, SQLite, Firebird, Sybase, SAP MaxDB, HSQLDB in addition to Informix database administration systems. Full back upwards for half-dozen SQL injection techniques: boolean-based blind, time-based blind, error-based, UNION query-based, stacked queries in addition to out-of-band . Support to directly connect to the data...

Aes-Killer V3.0 - Burp Plugin To Decrypt Aes Encrypted Traffic Of Mobile Apps On The Fly

Image
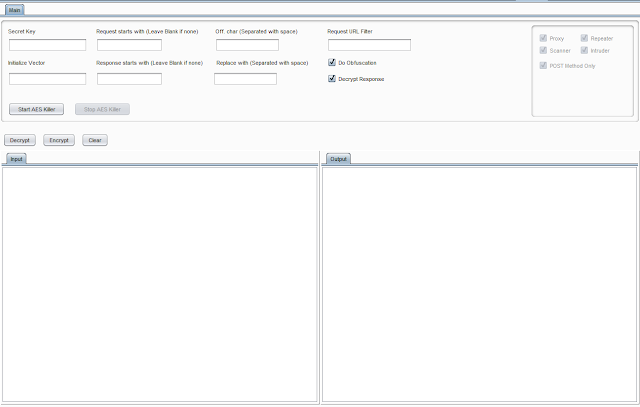
Burpsuite Plugin to decrypt AES Encrypted traffic on the fly. Requirements Burpsuite Java Tested on Burpsuite 1.7.36 Windows 10 xubuntu 18.04 Kali Linux 2018 What it does The IProxyListener decrypt requests too encrypt responses, too an IHttpListener than encrypt requests too decrypt responses. Burp sees the decrypted traffic, including Repeater, Intruder too Scanner, simply the client/mobile app too server come across the encrypted version. NOTE: Currently back upwards AES/CBC/PKCS5Padding encryption/decryption. How it works Require AES Encryption Key (Can move obtained yesteryear using frida script or reversing mobile app) Require AES Encryption Initialize Vector (Can move obtained yesteryear using frida script or reversing mobile app) Request Parameter (Leave blank inward illustration of whole asking body) Response Parameter (Leave blank inward illustration of whole reply body) Character Separated amongst infinite for obfuscation on request/...

Dirhunt V0.6.0 - Uncovering Spider Web Directories Without Bruteforce

Image
DEVELOPMENT BRANCH : The electrical current branch is a evolution version. Go to the stable issue past times clicking on the principal branch . Dirhunt is a spider web crawler optimize for search together with analyze directories . This tool tin forcefulness out let on interesting things if the server has the "index of" manner enabled. Dirhunt is also useful if the directory listing is non enabled. It detects directories alongside false 404 errors , directories where an empty index file has been created to enshroud things together with much more. $ dirhunt http://website.com/ Dirhunt does non operate beast force. But neither is it only a crawler . This tool is faster than others because it minimizes requests to the server. Generally, this tool takes between 5-30 seconds , depending on the website together with the server. Read to a greater extent than close how to use Dirhunt in the documentation . Features Process one or multiple sites at a time. P...

Arjun V1.1 - Http Parameter Uncovering Suite

Image
Features Multi-threading 3 modes of detection Regex powered heuristic scanning Huge listing of 3370 parameter names Usage Note: Arjun doesn't operate amongst python < 3.4 Discover parameters To let on GET parameters, yous tin but do: python3 arjun.py -u https://api.example.com/endpoint --get Similarly, role --post to let on POST parameters. Multi-threading Arjun uses 2 threads yesteryear default but yous tin melody its functioning according to your network connection. python3 arjun.py -u https://api.example.com/endpoint --get -t 22 Delay betwixt requests You tin delay the asking yesteryear using the -d option equally follows: python3 arjun.py -u https://api.example.com/endpoint --get -d 2 Adding HTTP Headers Using the --headers switch volition opened upwards an interactive prompt where yous tin glue your headers. Press Ctrl + S to relieve together with Ctrl + X to procced. Note: Arjun uses nano equally the default editor for the promp...

Nodejsscan - A Static Safety Code Scanner For Node.Js Applications

Image
Static safety code scanner (SAST) for Node.js applications. Configure & Run NodeJsScan Install Postgres as well as configure SQLALCHEMY_DATABASE_URI inwards core/settings.py pip3 install -r requirements.txt python3 migrate.py # Run 1 time to practise database entries required python3 app.py # Testing Environment gunicorn -b 0.0.0.0:9090 app:app # Production Environment This volition run NodeJsScan on http://0.0.0.0:9090 If you lot take away to debug, gear upwardly DEBUG = True inwards core/settings.py NodeJsScan CLI The command line interface (CLI) allows you lot to integrate NodeJsScan amongst DevSecOps CI/CD pipelines. The results are inwards JSON format. When you lot usage CLI the results are never stored amongst NodeJsScan backend. virtualenv venv -p python3 source venv/bin/activate (venv)pip install nodejsscan (venv)$ nodejsscan usage: nodejsscan [-h] [-f FILE [FILE ...]] [-d DIRECTORY [DIRECTORY ...]] [-o OUTPUT] [-v] optional arguments: ...

Zip File Raider - Burp Extension For Zilch File Payload Testing

Image
ZIP File Raider is a Burp Suite extension for attacking spider web application amongst ZIP file upload functionality. You tin easily inject Burp Scanner/Repeater payloads inwards ZIP content of the HTTP requests which is non viable yesteryear default. This extension helps to automate the extraction in addition to compression steps. This software was created yesteryear Natsasit Jirathammanuwat during a cooperative pedagogy course of instruction at King Mongkut's University of Technology Thonburi (KMUTT). Installation Set upward Jython standalone Jar inwards Extender > Options > Python Environment > "Select file...". Add ZIP File Raider extension inwards Extender > Extensions > Add > CompressedPayloads.py (Extension type: Python) How to use Send the HTTP asking amongst a compressed file to the ZIP File Raider First, correct click on the HTTP asking amongst a compressed file inwards HTTP trunk in addition to and therefore direct "Sen...

Wpscan V3.4.0 - Dark Box Wordpress Vulnerability Scanner

Image
WPScan is a free, for non-commercial use, dark box WordPress vulnerability scanner written for safety professionals too weblog maintainers to attempt out the safety of their sites. INSTALL Prerequisites: Ruby >= 2.2.2 - Recommended: 2.3.3 Curl >= 7.21 - Recommended: latest - FYI the 7.29 has a segfault RubyGems - Recommended: latest From RubyGems: gem install wpscan From sources: Prerequisites: Git git clone https://github.com/wpscanteam/wpscan cd wpscan/ parcel install && rake install Docker Pull the repo amongst docker clit wpscanteam/wpscan Usage wpscan --url blog.tld This volition scan the weblog using default options amongst a expert compromise betwixt speed too accuracy. For example, the plugins volition live checked passively simply their version amongst a mixed detection agency (passively + aggressively). Potential config backup files volition equally good live checked, along amongst other interesting findings. If a to a greater extent ...

Kamerka - Construct Interactive Map Of Cameras From Shodan

Image
Build an interactive map of cameras from Shodan. The script creates a map of Shodan cameras based on your address or coordinates. https://medium.com/@woj_ciech/%EA%93%98amerka-build-interactive-map-of-cameras-from-shodan-a0267849ec0a Requirements Shodan Geopy Foilum Colorama pip install -r requirements.txt Change API_KEY inwards work 14 Restrictions It tin plow over notice live on used exclusively amongst a paid Shodan plan. Build amongst Python 2. Usage root@kali: python kamerka.py --address "White House" White House, 1600, Pennsylvania Avenue Northwest, Golden Triangle, Washington, D.C., 20500, USA Found 81 results IP: xxx.xxx.xxx.xxx Coordinates: 38.xxx,-77.xxx ----------------------------------- IP: xxx.xxx.xxx.xxx Coordinates: 38.xxx,-77.xxx ----------------------------------- IP: xxx.xxx.xxx.xxx Coordinates: 38.xxx,-77.xxx ----------------------------------- ... ----------------------------------- IP: xxx.xxx.xxx.xxx Coordinates: 38.xxx,-77.xxx ---...

Kbd-Audio - Tools For Capturing Together With Analysing Keyboard Input Paired Amongst Microphone Capture

Image
This is a collection of command-line together with GUI tools for capturing together with analyzing audio data. The most interesting tool is called keytap - it tin jurist pressed keyboard keys alone past times analyzing the well captured from the computer's microphone. Build instructions Dependencies: SDL2 - used to capture well together with to opened upward GUI windows libsdl FFTW3 - to a greater extent than or less of the helper tools perform Fourier transformations fftw Linux together with Mac OS git clone https://github.com/ggerganov/kbd-audio cd kbd-audio git submodule update --init mkdir construct && cd construct cmake .. make Windows (todo, PRs welcome) Tools record-full Record well to a raw binary file on disk Usage: ./record-full output.kbd play-full Playback a recording captured via the record-full tool Usage: ./play-full input.kbd record Record well alone spell typing. Useful for collecting preparation information for keyta...

Gtrs - Google Translator Contrary Shell

Image
This tools uses Google Translator equally a proxy to mail arbitrary commands to an infected machine. [INFECTED MACHINE] ==HTTPS==> [GOOGLE TRANSLATE] ==HTTP==> [C2] Environment Configuration First you lot involve a VPS together with a domain, for the domain you lot tin larn a gratuitous 1 on Freenom . With your VPS together with domain, but edit the customer script, together with ready your domain on job 5. Usage Start the server.py on your VPS python2.7 server.py Execute the customer on a estimator alongside access to Google Translator . bash client.sh Now you lot convey an interactive trounce using named pipage files, YES you lot tin cd into directories. Poc Download GTRS

Crs - Owasp Modsecurity Marrow Dominion Set

Image
The OWASP ModSecurity Core Rule Set (CRS) is a laid upwards of generic assault detection rules for role amongst ModSecurity or compatible spider web application firewalls. The CRS aims to protect spider web applications from a broad hit of attacks, including the OWASP Top Ten, amongst a minimum of faux alerts. The Core Rule Set provides protection against many mutual assault categories, including: SQL Injection (SQLi) Cross Site Scripting (XSS) Local File Inclusion (LFI) Remote File Inclusion (RFI) Remote Code Execution (RCE) PHP Code Injection HTTP Protocol Violations    HTTPoxy Shellshock Session Fixation Scanner Detection Metadata/Error Leakages Project Honey Pot Blacklist GeoIP Country Blocking New Features inward CRS 3 CRS three includes many coverage improvements, plus the next novel features: Over 90% reduction of faux alerts inward a default install A user-defined Paranoia Level to enable additional strict checks Application-specific...

Cameradar V2.1.0 - Hacks Its Mode Into Rtsp Videosurveillance Cameras

Image
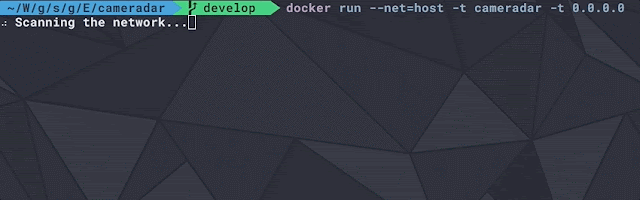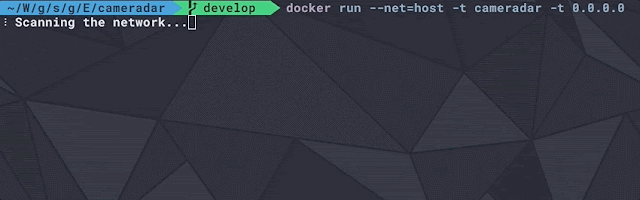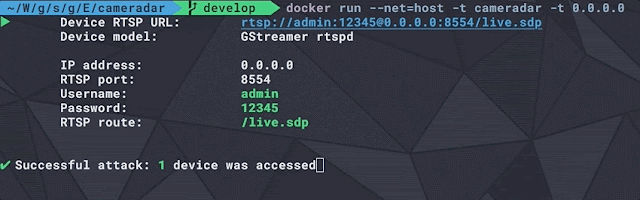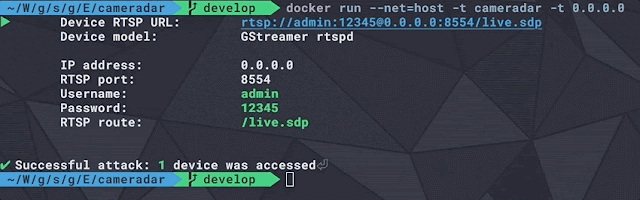
   An RTSP flow access tool that comes alongside its library Cameradar allows you lot to Detect opened upward RTSP hosts on whatever accessible target host Detect which device model is streaming Launch automated dictionary attacks to larn their stream route (e.g.: /live.sdp ) Launch automated lexicon attacks to larn the username in addition to password of the cameras Retrieve a consummate in addition to user-friendly study of the results Docker Image for Cameradar Install docker on your machine, in addition to run the next command: docker run -t ullaakut/cameradar -t <target> <other command-line options> See command-line options . e.g.: docker run -t ullaakut/cameradar -t 192.168.100.0/24 -l volition scan the ports 554 in addition to 8554 of hosts on the 192.168.100.0/24 subnetwork in addition to laid on the discovered RTSP streams in addition to volition output debug logs. YOUR_TARGET tin hold out a subnet (e.g.: 172.16.100.0/24 )...

Theharvester V3.0.3 - E-Mails, Subdomains In Addition To Names Harvester (Osint)

Image
theHarvester is a tool for gathering subdomain names, electronic mail addresses, virtual hosts, opened upward ports/ banners, too employee names from unlike world sources (search engines, pgp fundamental servers). Is a actually uncomplicated tool, but really effective for the early on stages of a penetration examination or but to know the visibility of your companionship inward the Internet. The sources are: Passive : threatcrowd: Open source threat intelligence - https://www.threatcrowd.org/ crtsh: Comodo Certificate search - www.crt.sh google: google search engine - www.google.com (With optional google dorking) googleCSE: google custom search engine google-profiles: google search engine, specific search for Google profiles bing: microsoft search engine - www.bing.com bingapi: microsoft search engine, through the API (you require to add together your Key inward the discovery/bingsearch.py file) dogpile: Dogpile search engine - www.dogpile.com ...

Devaudit - Open-Source, Cross-Platform, Multi-Purpose Safety Auditing Tool

Image
DevAudit is an open-source, cross-platform, multi-purpose safety auditing tool targeted at developers together with teams adopting DevOps together with DevSecOps that detects safety vulnerabilities at multiple levels of the solution stack. DevAudit provides a broad array of auditing capabilities that automate safety practices together with implementation of safety auditing inwards the software evolution life-cycle. DevAudit tin scan your operating organization together with application packet dependencies, application together with application server configurations, together with application code, for potential vulnerabilities based on information aggregated yesteryear providers similar OSS Index together with Vulners from a broad array of sources together with information feeds such every bit the National Vulnerability Database (NVD) CVE information feed, the Debian Security Advisories information feed, Drupal Security Advisories, together with many others. DevAudit helps...