Posts

Showing posts with the label Packets

Isip - Interactive Drink Toolkit For Bundle Manipulations, Sniffing, Human Inwards The Meat Attacks, Fuzzing, Simulating Of Dos Attacks
Image
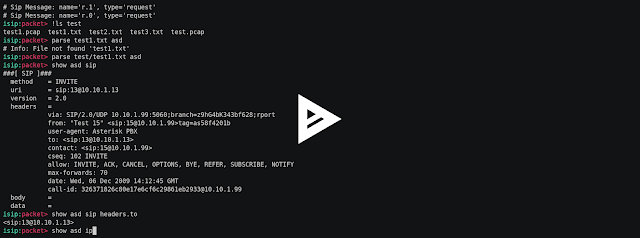
Interactive gulp toolkit for parcel manipulations, sniffing, man inwards the middle attacks, fuzzing, simulating of dos attacks. Video Setup git clone https://github.com/halitalptekin/isip.git cd isip pip install -r requirements.txt Usage Packet manipulation tools are inwards packet cmd loop. First start, you lot are inwards the main cmd loop. isip:main> parcel isip:packet> Create a novel gulp parcel amongst new command. If you lot don't write name, isip practise the parcel named yesteryear message-{id} . isip:packet> novel isip:packet> novel r1 List the all created gulp packets amongst list command. isip:packet> list Show properties of packets amongst show command. You tin type ip , udp or sip amongst show command. isip:packet> present message-1 isip:packet> present message-1 ip isip:packet> present message-1 udp isip:packet> present message-1 gulp isip:packet> present message-1 ip src isip:packet> pre...
Sniffair - A Framework For Wireless Pentesting

Image
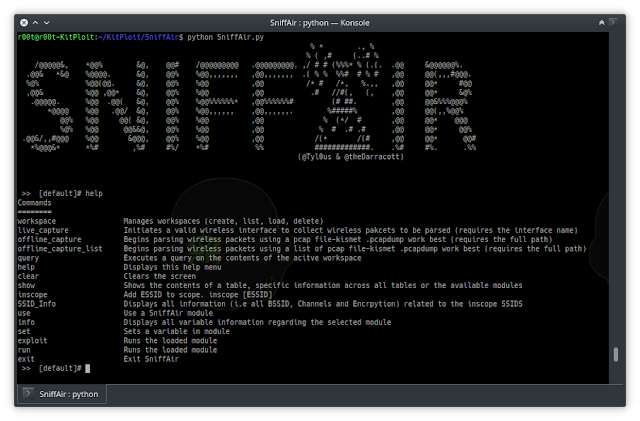
SniffAir is an open-source wireless safety framework which provides the mightiness to easily parse passively collected wireless information every bit good every bit launch sophisticated wireless attacks. SniffAir takes aid of the hassle associated alongside managing large or multiple pcap files land thoroughly cross-examining as well as analyzing the traffic, looking for potential safety flaws. Along alongside the prebuilt queries, SniffAir allows users to exercise custom queries for analyzing the wireless information stored inward the backend SQL database. SniffAir is built on the concept of using these queries to extract information for wireless penetration test reports. The information tin every bit good survive leveraged inward setting upwards sophisticated wireless attacks included inward SniffAir every bit modules. SniffAir is developed past times @Tyl0us as well as @theDarracott Install SniffAir was developed alongside Python version 2.7 Tested as well as supported o...

Tcpreplay - Pcap Editing Together With Replay Tools For *Nix Together With Windows

Image
Tcpreplay is a suite of GPLv3 licensed utilities for UNIX (and Win32 nether Cygwin ) operating systems for editing as well as replaying network traffic which was previously captured past times tools similar tcpdump as well as Ethereal / Wireshark . It allows y'all to separate traffic equally customer or server, rewrite Layer 2, iii as well as four packets as well as in conclusion replay the traffic dorsum onto the network as well as through other devices such equally switches, routers, firewalls, NIDS as well as IPS's. Tcpreplay supports both unmarried as well as dual NIC modes for testing both sniffing as well as in-line devices. Tcpreplay is used past times numerous firewall, IDS, IPS, NetFlow as well as other networking vendors, enterprises, universities, labs as well as opened upwardly source projects. If your organization uses Tcpreplay, delight allow us know who y'all are as well as what y'all purpose it for as well as so that I tin proceed to add togethe...

Netsniff-Ng - A Swiss Regular Army Knife For Your Daily Linux Network Plumbing

Image
netsniff-ng is a gratuitous Linux networking toolkit, a Swiss terra firma forces knife for your daily Linux network plumbing if you lot will. Its gain of functioning is reached yesteryear zero-copy mechanisms, so that on parcel reception and transmission the gist does non involve to re-create packets from gist infinite to user infinite in addition to vice versa. Our toolkit tin move used for network evolution in addition to analysis, debugging, auditing or network reconnaissance. The netsniff-ng toolkit consists of the next utilities: netsniff-ng , a fast zero-copy analyzer, pcap capturing in addition to replaying tool trafgen , a multithreaded low-level zero-copy network parcel generator mausezahn , high-level parcel generator for HW/SW appliances amongst Cisco-CLI* bpfc , a Berkeley Packet Filter compiler, Linux BPF JIT disassembler ifpps , a top-like gist networking statistics tool flowtop , a top-like netfilter connector tracking tool curvetun , a lightweight ...

Canalyzat0r - Safety Analysis Toolkit For Proprietary Car Protocols

Image
This software projection is a resultant of a Bachelor's thesis created at SCHUTZWERK inwards collaboration amongst Aalen University past times Philipp Schmied. Please refer to the corresponding blog post for to a greater extent than information. Why about other CAN tool? Built from scratch amongst novel ideas for analysis mechanisms Bundles features of many other tools inwards 1 place Modular as well as extensible: Read the docs as well as implement your ain analysis mechanisms Comfortable analysis using a GUI Manage locomote inwards split projects using a database Documentation: Read the docs if you lot demand a manual or technical info. Installing as well as running: Run sudo ./install_requirements.sh along amongst sudo -E ./CANalyzat0r.sh . This volition produce a folder called pipenv amongst a pipenv surroundings inwards it. Or only purpose the docker version which is recommended at this fourth dimension (Check the README.md file inwards the subdire...

Bonesi - The Ddos Botnet Simulator

Image
BoNeSi , the DDoS Botnet Simulator is a Tool to copy Botnet Traffic inward a testbed surroundings on the wire. It is designed to report the final result of DDoS attacks. What traffic tin hold out generated? BoNeSi generates ICMP, UDP too TCP (HTTP) flooding attacks from a defined botnet size (different IP addresses). BoNeSi is highly configurable too rates, information volume, source IP addresses, URLs too other parameters tin hold out configured. What makes it dissimilar from other tools? There are enough of other tools out at that spot to spoof IP addresses amongst UDP too ICMP, but for TCP spoofing, at that spot is no solution. BoNeSi is the commencement tool to copy HTTP-GET floods from large-scale bot networks. BoNeSi also tries to avoid to generate packets amongst tardily identifiable patterns (which tin hold out filtered out easily). Where tin I run BoNeSi ? We highly recommend to run BoNeSi inward a unopen testbed environment. However, UDP too ...

Pfq - Functional Network Framework For Multi-Core Architectures

Image
PFQ is a functional framework designed for the Linux operating arrangement built for efficient packets capture/transmission (10G, 40G too beyond), in-kernel functional processing, kernel-bypass too packets steering across groups of sockets/end-points. It is highly optimized for multi-core architecture, equally good equally for network devices equipped amongst multiple hardware queues. Compliant amongst whatsoever NIC, it provides a script that generates accelerated network device drivers starting from the source code. PFQ enables the evolution of high-performance network applications, too it is shipped amongst a custom version of libpcap that accelerate too parallelize legacy applications. Besides, a pure functional linguistic communication designed for early on stages in-kernel package processing is included: pfq-lang. Pfq-Lang is inspired yesteryear Haskell too is intended to define applications that run on top of network device drivers. Through pfq-lang it is possible to ...

Mutiny Fuzzing Framework - Network Fuzzer That Operates Past Times Replaying Pcaps Through A Mutational Fuzzer

Image
The Mutiny Fuzzing Framework is a network fuzzer that operates yesteryear replaying PCAPs through a mutational fuzzer. The destination is to start network fuzzing every bit apace every bit possible, at the expense of existence thorough. The full general workflow for Mutiny is to accept a sample of legitimate traffic, such every bit a browser request, as well as feed it into a prep script to generate a .fuzzer file. Then, Mutiny tin survive run with this .fuzzer file to generate traffic against a target host, mutating whichever packets the user would like. There are extensions that let changing how Mutiny behaves, including changing messages based on input/output, changing how Mutiny responds to network errors, as well as monitoring the target inwards a split thread. Mutiny uses Radamsa to perform mutations. The Decept Proxy is a multi-purpose network proxy that tin forrad traffic from a plaintext or TLS TCP/UDP/domain socket connexion to a plaintext or TLS TCP/UDP/d...

Mongobuster - Hunt Opened Upward Mongodb Instances

Image
Hunt Open MongoDB instances! Features Worlds fastest too virtually efficient scanner ( Uses Masscan ). Scans entire cyberspace past times default, So burn downward the tool too chill. Hyper efficient - Uses Go-routines which are fifty-fifty lighter than threads. Pre-Requisites - Go linguistic communication ( sudo apt install golang ) Masscan ( sudo apt install masscan ) Tested on Ubuntu & Kali linux How to install too run - git clone https://github.com/yashpl/mongoBuster.git cd mongoBuster larn laid upwards mongobuster.go utils.go sudo ./mongobuster Note: Run it amongst sudo every bit Masscan requires sudo access. Flags - Flag Description --max-rate= (int) Defines maximum charge per unit of measurement at which packets are generated too sent. Default is 100. --out-file= (string) Name of file to which vulnerable IPs volition last exported. -v Display fault msgs from non-vulnerable servers NOTE - Using ridiculous values fo...

Termshark - A Final Ui For Tshark, Inspired Past Times Wireshark

Image
H5N1 finally user-interface for tshark, inspired past times Wireshark. If you're debugging on a remote automobile amongst a large pcap together with no wishing to scp it dorsum to your desktop, termshark tin give notice help! Features Read pcap files or sniff alive interfaces (where tshark is permitted). Inspect each packet using familiar Wireshark-inspired views Filter pcaps or alive captures using Wireshark's display filters Copy ranges of packets to the clipboard from the terminal Written inward Golang, compiles to a unmarried executable on each platform - downloads available for Linux (+termux), macOS, FreeBSD, together with Windows tshark has many to a greater extent than features that termshark doesn't bring out yet! See What's Next . Installation (FreeBSD) Termshark is inward the FreeBSD ports tree! To install the package, run: pkg install termshark To build/install the port, run: cd /usr/ports/net/termshark/ && brand insta...

Dnslivery - Slowly Files Together With Payloads Delivery Over Dns

Image
Easy files in addition to payloads delivery over DNS. Acknowledgments This projection has been originally inspired past times PowerDNS in addition to Joff Thyer 's technical segment on the Paul's Security Weekly podcast #590 ( youtu.be/CP6cIwFJswQ ). Description TL;DR DNSlivery allows delivering files to a target using DNS equally the carry protocol. Features : allows to print, execute or salve files to the target does non require whatever customer on the target does non require a full-fledged DNS server  What work are y'all trying to solve? Easily deliver files and/or payloads to a compromised target where classic spider web delivery is non possible in addition to without the take away for a dedicated customer software . This applies to restricted environments where outgoing spider web traffic is forbidden or precisely inspected past times a curious spider web proxy. Even though to a greater extent than consummate DNS tunneling tools already be (...